
350-501 · Question #395
Refer to the exhibit. The radio network and packet core are using the route RX-RZ-RB to establish communication. The LDP session between 10.10.10.5 and 10.10.10.1 is experiencing link flapping at…
The correct answer is C. Add session protection duration 60 for peer_acl_1 under the MPLS LDP instance on RZ. The LDP session between RX and RZ is flapping for 30-45 seconds, requiring protection and improved MPLS convergence. Configuring LDP session protection with a duration greater than the flap interval (e.g., 60 seconds) will keep the LDP session and its labels active during the…
Question
Refer to the exhibit. The radio network and packet core are using the route RX-RZ-RB to establish communication. The LDP session between 10.10.10.5 and 10.10.10.1 is experiencing link flapping at random intervals for 30-45 seconds each time. A network engineer must protect the LDP session and improve MPLS traffic convergence. Which action meets these requirements?
Exhibit
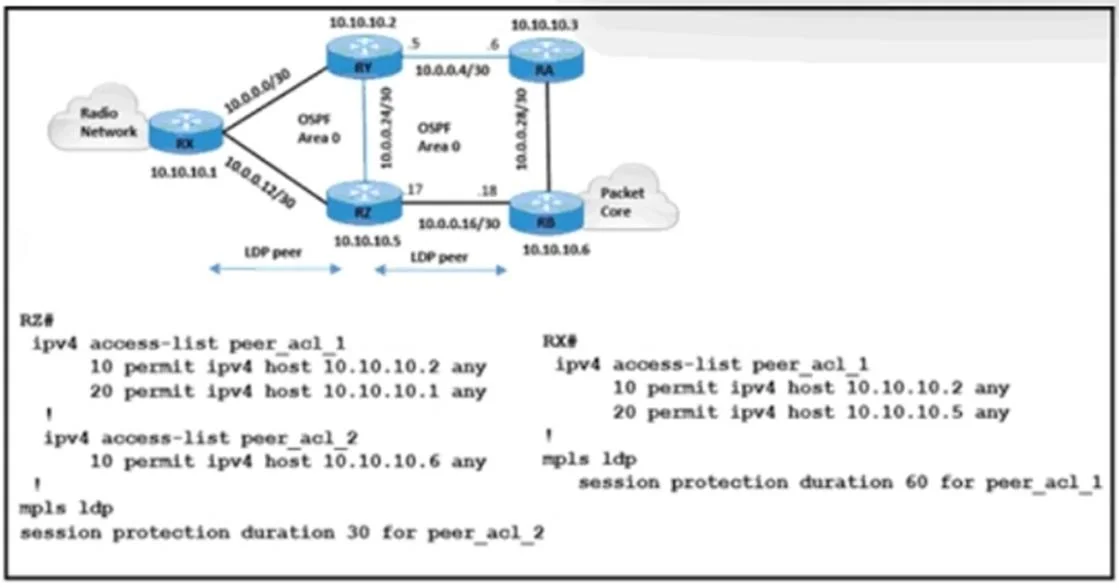
Options
- AConfigure peer_acl_2 on RX and allow IP address 10.10.10.6 in LDP.
- BAttach peer_acl_1 in for session protection duration 1 on RX.
- CAdd session protection duration 60 for peer_acl_1 under the MPLS LDP instance on RZ.
- DEnable IGP-LDP sync on RZ and RX.
How the community answered
(37 responses)- A5% (2)
- B16% (6)
- C73% (27)
- D5% (2)
Why each option
The LDP session between RX and RZ is flapping for 30-45 seconds, requiring protection and improved MPLS convergence. Configuring LDP session protection with a duration greater than the flap interval (e.g., 60 seconds) will keep the LDP session and its labels active during the temporary outages, ensuring continuous MPLS traffic forwarding.
Configuring an access list to allow an IP address in LDP is for controlling which peers can form LDP sessions, not for protecting an existing, flapping session.
While the action type is correct, a session protection duration of 1 second is insufficient to protect against link flaps lasting 30-45 seconds.
LDP Session Protection allows the LDP session to remain operational and labels to be preserved for a configured duration even if the underlying IGP adjacency or LDP control plane temporarily fails. Setting `session protection duration 60` for the peer on RZ will keep the LDP session active and prevent traffic disruption during the 30-45 second link flaps, thereby improving MPLS traffic convergence.
IGP-LDP synchronization is used to prevent traffic blackholing by delaying IGP route advertisement until LDP is fully operational on a link, not to protect an LDP session during link flaps.
Concept tested: LDP Session Protection configuration
Source: https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/mpls/configuration/xe-3s/mp-xe-3s-book/mp-ldp-sess-prot.html
Topics
Community Discussion
No community discussion yet for this question.