
350-501 · Question #197
Refer to the exhibit. To protect in-band management access to CPE-R7, an engineer wants to allow only SSH management and provisioning traffic from management network 192.168.0.0/16. Which…
The correct answer is B. ip access-list extended INFRA-ACL. The infrastructure ACL must specifically permit SSH traffic from the management network to CPE-R7, explicitly deny all other traffic to CPE-R7, and then permit all other legitimate transit traffic through PE-R9.
Question
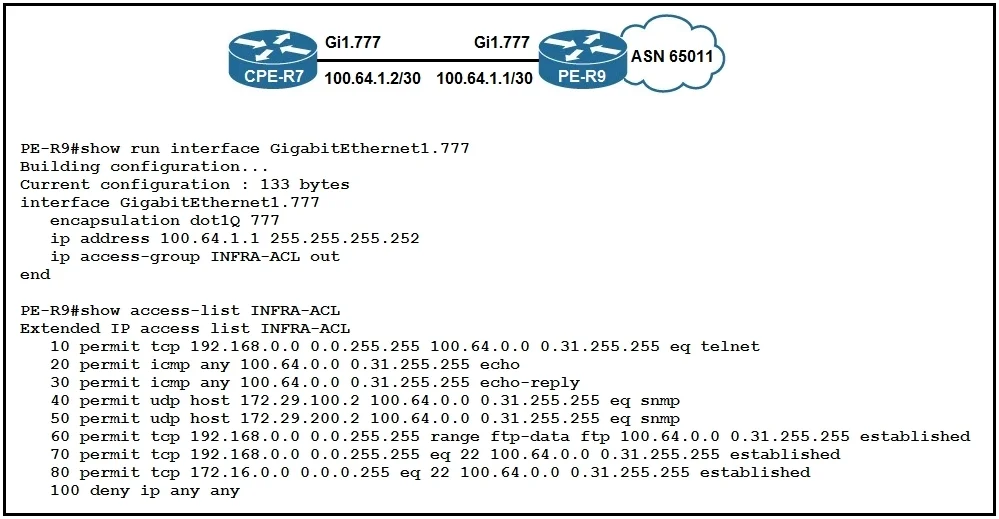
Refer to the exhibit. To protect in-band management access to CPE-R7, an engineer wants to allow only SSH management and provisioning traffic from management network 192.168.0.0/16. Which infrastructure ACL change must be applied to router PE-R9 to complete this task?
Exhibit
Options
- Aip access-list extended INFRA-ACL
- Bip access-list extended INFRA-ACL
- Cip access-list extended INFRA-ACL
- Dip access-list extended INFRA-ACL
How the community answered
(55 responses)- A5% (3)
- B71% (39)
- C16% (9)
- D7% (4)
Why each option
The infrastructure ACL must specifically permit SSH traffic from the management network to CPE-R7, explicitly deny all other traffic to CPE-R7, and then permit all other legitimate transit traffic through PE-R9.
While it permits SSH and then denies other IP traffic to CPE-R7, it lacks the 'permit ip any any' at the end, which would implicitly deny all other transit traffic through PE-R9, likely disrupting other network services.
This ACL first permits TCP SSH traffic (port 22) from the 192.168.0.0/16 management network to CPE-R7 (assumed 10.1.1.7). The subsequent 'deny ip any host 10.1.1.7 log' explicitly denies all other IP traffic to CPE-R7, fulfilling the 'allow only SSH' requirement for that device. Finally, 'permit ip any any' allows all other non-CPE-R7-bound transit traffic to flow through PE-R9, which is crucial for its role as a network router.
This ACL starts by explicitly denying TCP SSH traffic to CPE-R7, which directly contradicts the requirement to allow it.
This ACL permits SSH traffic from any source, not just the specified 192.168.0.0/16 management network, making the protection less granular. It also has an implicit 'deny ip any any' at the end which would block all other transit traffic.
Concept tested: Infrastructure ACL (iACL) configuration for device protection
Source: https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/security/dpa/configuration/xe-3s/sec-dpa-xe-3s-book/sec-acl-best-pract.html
Topics
Community Discussion
No community discussion yet for this question.