
312-50V10 · Question #691
Take a look at the following attack on a Web Server using obstructed URL: How would you protect from these attacks?
The correct answer is B. Create rules in IDS to alert on strange Unicode requests. Obfuscated URL attacks use hex or Unicode encoding to evade simple pattern-based filters. The best defense is IDS rules that detect anomalous encoding patterns in HTTP requests.
Question
Take a look at the following attack on a Web Server using obstructed URL:
How would you protect from these attacks?
Exhibit
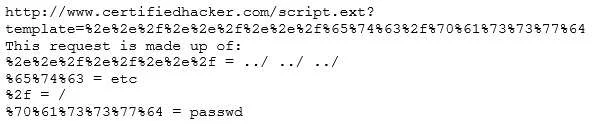
Options
- AConfigure the Web Server to deny requests involving "hex encoded" characters
- BCreate rules in IDS to alert on strange Unicode requests
- CUse SSL authentication on Web Servers
- DEnable Active Scripts Detection at the firewall and routers
How the community answered
(57 responses)- A16% (9)
- B74% (42)
- C4% (2)
- D7% (4)
Why each option
Obfuscated URL attacks use hex or Unicode encoding to evade simple pattern-based filters. The best defense is IDS rules that detect anomalous encoding patterns in HTTP requests.
Blocking all hex-encoded characters would break legitimate web traffic because percent-encoding is a standard and required part of the URI specification for many valid requests.
An IDS configured with rules to detect unusual Unicode or percent-encoded character sequences in HTTP requests can identify and alert on URL obfuscation attempts in real time. This approach catches evasion techniques that bypass naive string-matching filters, allowing security teams to investigate and block malicious traffic. It addresses the root behavior - encoding used to disguise attack payloads - rather than surface-level symptoms.
SSL authentication secures the transport layer and verifies identity, but it does not inspect or block malformed or obfuscated URL paths sent inside the encrypted session.
Active Scripts Detection at the firewall targets script execution attempts, not URL encoding obfuscation, so it would not detect or prevent this specific attack vector.
Concept tested: IDS detection of URL obfuscation attacks
Source: https://owasp.org/www-community/attacks/Unicode_Encoding
Topics
Community Discussion
No community discussion yet for this question.