
300-715 · Question #164
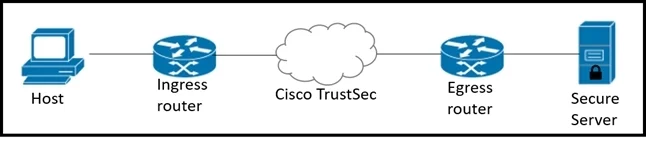
Refer to the exhibit. Which component must be configured to apply the SGACL?
The correct answer is A. egress router. In Cisco TrustSec, SGACLs (Security Group Access Control Lists) are enforced at the egress router - the device closest to the destination of the traffic. The TrustSec architecture works as follows: the ingress router tags traffic with a Security Group Tag (SGT) as it enters the…
Question
Refer to the exhibit. Which component must be configured to apply the SGACL?
Exhibit
Options
- Aegress router
- Bhost
- Csecure server
- Dingress router
How the community answered
(32 responses)- A91% (29)
- C3% (1)
- D6% (2)
Explanation
In Cisco TrustSec, SGACLs (Security Group Access Control Lists) are enforced at the egress router - the device closest to the destination of the traffic. The TrustSec architecture works as follows: the ingress router tags traffic with a Security Group Tag (SGT) as it enters the TrustSec domain, and the egress router uses that tag to apply the appropriate SGACL policy as traffic exits toward its destination. The egress enforcement point is where access decisions (permit/deny) are actually applied based on source and destination SGTs.
Topics
Community Discussion
No community discussion yet for this question.