
300-620 · Question #294
Refer to the exhibit. A network engineer must improve the configuration backup process and the configuration restore process. The current ACI solution is integrated with VMMs and third-party L4-L7…
The correct answer is B. Enable the Global AES Encryption Setting. To ensure a configuration backup can be fully restored without requiring re-entry of sensitive information, especially when integrating with VMMs and L4-L7 devices, enabling the Global AES Encryption Setting is crucial.
Question
Refer to the exhibit. A network engineer must improve the configuration backup process and the configuration restore process. The current ACI solution is integrated with VMMs and third-party L4-L7 devices. The process requires that no additional information be re-entered when importing the configuration for a fully-functional state. Which configuration configures the export policy?
Exhibit
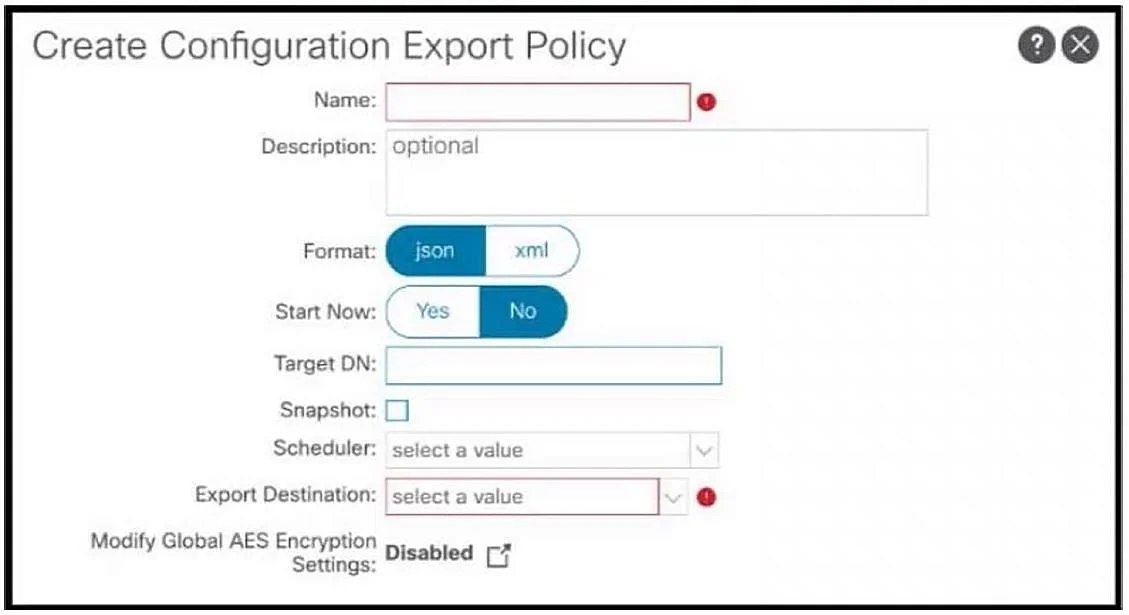
Options
- AConfigure a local snapshot.
- BEnable the Global AES Encryption Setting.
- CSelect the JSON data format to be used when exporting.
- DCreate target DNs for all tenants.
How the community answered
(40 responses)- A5% (2)
- B88% (35)
- C3% (1)
- D5% (2)
Why each option
To ensure a configuration backup can be fully restored without requiring re-entry of sensitive information, especially when integrating with VMMs and L4-L7 devices, enabling the Global AES Encryption Setting is crucial.
Configuring a local snapshot creates a backup, but it doesn't inherently address the requirement of not re-entering sensitive information during a restore, as snapshots typically don't encrypt embedded credentials unless explicitly configured.
Enabling the Global AES Encryption Setting ensures that sensitive information, such as login credentials for VMMs and L4-L7 devices, is encrypted within the configuration backup. This encryption allows the entire configuration, including these sensitive details, to be imported and restored without requiring manual re-entry, thus achieving a fully functional state post-restore.
Selecting the JSON data format for export defines how the configuration data is structured, but it does not provide encryption for sensitive information to prevent re-entry during restore.
Creating target DNs for all tenants is a configuration step within ACI but is unrelated to the encryption of sensitive data within a backup to facilitate a full restore without manual re-entry.
Concept tested: ACI secure configuration backup restore
Source: https://www.cisco.com/c/en/us/td/docs/dcn/aci/apic/5x/sw-install/b_Cisco_APIC_Software_Installation_Upgrade_Downgrade_Guide_5x/b_Cisco_APIC_Software_Installation_Upgrade_Downgrade_Guide_5x_chapter_01.html
Topics
Community Discussion
No community discussion yet for this question.