
300-215 · Question #132
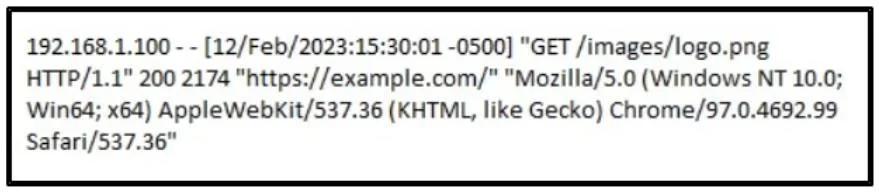
Refer to the exhibit. A cybersecurity analyst must analyze the logs from an Apache server for the client. The concern is that an offboarded employee home IP address was potentially used to access…
The correct answer is D. An employee has accessed a web page on the server. The log shows an HTTP GET request that returned 200 OK for “/images/logo.png” from the client IP, indicating the client successfully requested content from the web server. This is consistent with access to a web resource (page content and its referenced objects) rather than an…
Question
Refer to the exhibit. A cybersecurity analyst must analyze the logs from an Apache server for the client. The concern is that an offboarded employee home IP address was potentially used to access the company web server via a still active VPN connection. Based on this log entry, what should an analyst conclude?
Exhibit
Options
- AA worker uploaded a file to the server.
- BAn ex employee planted malware on the server.
- CA file was downloaded from the server.
- DAn employee has accessed a web page on the server.
How the community answered
(24 responses)- A4% (1)
- B4% (1)
- C8% (2)
- D83% (20)
Explanation
The log shows an HTTP GET request that returned 200 OK for “/images/logo.png” from the client IP, indicating the client successfully requested content from the web server. This is consistent with access to a web resource (page content and its referenced objects) rather than an upload or proof of malware placement.
Topics
Community Discussion
No community discussion yet for this question.