
300-215 · Question #131
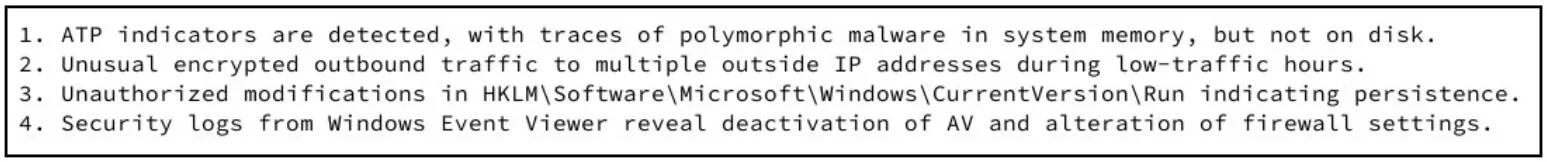
Refer to the exhibit. An experienced cybersecurity analyst is investigating a sophisticated suspected breach on a Windows server within an enterprise network and compiled the evidence gathered so…
The correct answer is B. Perform a forensic memory analysis to isolate and identify the polymorphic malware's behavior. When polymorphic malware is present in memory but not on disk, memory forensics is the fastest way to confirm what is running, how it is executing, what it is injecting into, and what it is doing (processes, loaded modules, network connections, decrypted payloads, and in-memory…
Question
Refer to the exhibit. An experienced cybersecurity analyst is investigating a sophisticated suspected breach on a Windows server within an enterprise network and compiled the evidence gathered so far. Which action should the analyst prioritize to understand the scope and impact of the breach?
Exhibit
Options
- AReview the security log alterations to understand the methods used to deactivate security systems.
- BPerform a forensic memory analysis to isolate and identify the polymorphic malware's behavior
- CConduct a deep dive analysis of the outbound network traffic to trace the foreign IP addresses.
- DInvestigate the Windows Registry modifications for potential backdoors and establish a timeline of
How the community answered
(26 responses)- A23% (6)
- B62% (16)
- C4% (1)
- D12% (3)
Explanation
When polymorphic malware is present in memory but not on disk, memory forensics is the fastest way to confirm what is running, how it is executing, what it is injecting into, and what it is doing (processes, loaded modules, network connections, decrypted payloads, and in-memory artifacts). This provides high-confidence indicators and behavioral context needed to accurately determine scope and impact before drilling into secondary artifacts like registry, logs, or traffic.
Topics
Community Discussion
No community discussion yet for this question.