
300-170 · Question #118
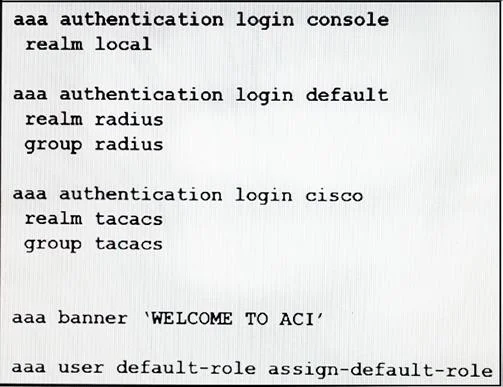
Refer to the exhibit. Which result occurs when a user without a role attempts to log into the fabric?
The correct answer is C. The user is assigned to a default role. When a user successfully authenticates into the ACI fabric but has no specific role assigned, they are granted permissions defined by a default role.
Question
Refer to the exhibit. Which result occurs when a user without a role attempts to log into the fabric?
Exhibit
Options
- AThe user is denied access
- BThe user is assigned to the local domain
- CThe user is assigned to a default role
- DThe user is authenticated by using TACACS
How the community answered
(65 responses)- A9% (6)
- B8% (5)
- C80% (52)
- D3% (2)
Why each option
When a user successfully authenticates into the ACI fabric but has no specific role assigned, they are granted permissions defined by a default role.
Access is typically denied only if the authentication process itself fails or if the user is explicitly denied access through a role mapping.
The 'local domain' refers to local authentication on the APIC, not a role that is assigned after authentication when no explicit role is found.
Cisco ACI's authentication and authorization model assigns a default role to users who successfully authenticate but do not have an explicitly configured role mapping. This default role typically provides very limited, often read-only, access to prevent unauthorized configuration changes while allowing some visibility.
Authentication by using TACACS is a method of verifying user credentials, which occurs before role assignment; the question asks what happens after authentication if no role is found.
Concept tested: ACI user roles and authentication
Source: https://www.cisco.com/c/en/us/td/docs/switches/datacenter/aci/apic/sw/1-x/security/b_Cisco_ACI_Security_Configuration_Guide/b_Cisco_ACI_Security_Configuration_Guide_chapter_010.html
Topics
Community Discussion
No community discussion yet for this question.