
200-901 · Question #214
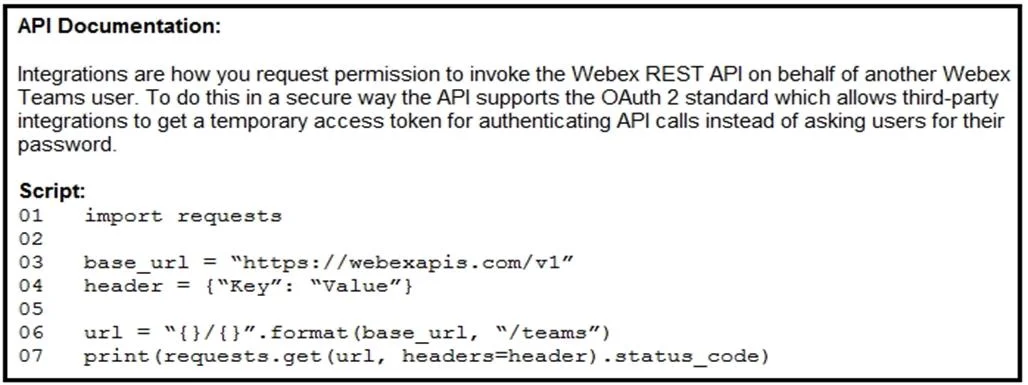
Refer to the exhibit. A developer creates a Python script that queries Cisco Webex. When the script is executed, a 401 code is returned. After troubleshooting, the developer discovers that the…
The correct answer is D. header = {"Authorization" : "Bearer YOUR_TOKEN"}. To correct a 401 Unauthorized error when querying a REST API, the HTTP request header must use the Authorization field with the Bearer token scheme to properly authenticate the request.
Question
Refer to the exhibit. A developer creates a Python script that queries Cisco Webex. When the script is executed, a 401 code is returned. After troubleshooting, the developer discovers that the service is missing privileges. Which change to the header in line 4 of the script results in the code 200?
Exhibit
Options
- Aheader = {"Authentication": "Bearer YOUR_TOKEN"}
- Bheader = {"Authentication Bearer" : "YOUR_TOKEN"
- Dheader = {"Authorization" : "Bearer YOUR_TOKEN"}
How the community answered
(39 responses)- A3% (1)
- B10% (4)
- D87% (34)
Why each option
To correct a 401 Unauthorized error when querying a REST API, the HTTP request header must use the `Authorization` field with the `Bearer` token scheme to properly authenticate the request.
The header key `Authentication` is not the standard HTTP header for sending bearer tokens; the correct header field is `Authorization`.
`Authentication Bearer` is not a valid HTTP header key; the standard is `Authorization` followed by the scheme and credentials.
A 401 Unauthorized error typically indicates missing or incorrect authentication credentials. The standard HTTP header for sending authentication tokens, especially bearer tokens, is `Authorization`, with the value formatted as `Bearer YOUR_TOKEN`. This correct header provides the necessary credentials for the API to grant access, leading to a 200 OK response if privileges are sufficient.
Concept tested: REST API authentication - HTTP Authorization header
Source: https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/Authorization
Topics
Community Discussion
No community discussion yet for this question.