
200-901 · Question #199
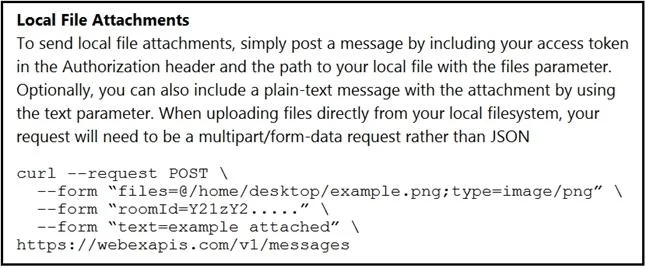
Refer to the exhibit. A developer needs to upload a local file by using the REST API. The developer gathers information according to the documentation and sends the request by using the cURL command…
The correct answer is B. add the authorization header with the access token. The most common cause of an error when accessing a REST API without any authentication-related header is an HTTP 401 Unauthorized response. The fix is to add an Authorization header containing the access token (e.g., 'Authorization: Bearer <token>'). Option A is wrong because…
Question
Refer to the exhibit. A developer needs to upload a local file by using the REST API. The developer gathers information according to the documentation and sends the request by using the cURL command in the exhibit but gets an error code. Which action should be followed to get a valid response?
Exhibit
Options
- Achange content-type as JSON
- Badd the authorization header with the access token
- Cand a username-password combination to request command
- Dchange request method as GET
How the community answered
(19 responses)- A5% (1)
- B89% (17)
- D5% (1)
Explanation
The most common cause of an error when accessing a REST API without any authentication-related header is an HTTP 401 Unauthorized response. The fix is to add an Authorization header containing the access token (e.g., 'Authorization: Bearer <token>'). Option A is wrong because changing Content-Type to JSON would not fix an authentication error, and file uploads typically use multipart/form-data. Option C (username-password) may apply to Basic Auth, but when an API uses token-based auth, an access token header is the correct approach. Option D is wrong because uploading a file requires a POST/PUT, not GET.
Topics
Community Discussion
No community discussion yet for this question.