
200-901 · Question #161
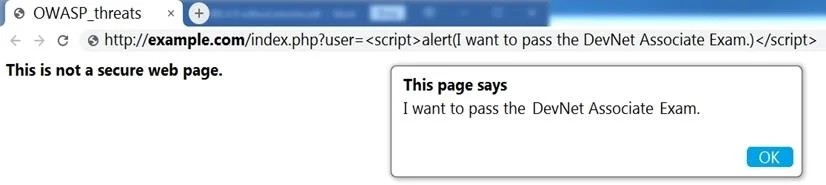
Refer to the exhibit. Which OWASP threat does this example demonstrate?
The correct answer is D. cross-site scripting. Cross-site scripting (XSS) involves injecting malicious client-side scripts into web content that is then executed in other users' browsers. It is listed in the OWASP Top 10 as a critical web application vulnerability caused by insufficient input validation and output encoding.
Question
Refer to the exhibit. Which OWASP threat does this example demonstrate?
Exhibit
Options
- Abroken access control
- BSQL injection
- Cman-in-the-middle
- Dcross-site scripting
How the community answered
(44 responses)- A16% (7)
- B9% (4)
- C5% (2)
- D70% (31)
Why each option
Cross-site scripting (XSS) involves injecting malicious client-side scripts into web content that is then executed in other users' browsers. It is listed in the OWASP Top 10 as a critical web application vulnerability caused by insufficient input validation and output encoding.
Broken access control refers to failures in enforcing authorization restrictions on authenticated users - such as accessing other users' records or performing privileged actions - not script injection into rendered web content.
SQL injection involves inserting malicious SQL statements into input fields to manipulate a backend database, which is a server-side data attack rather than a client-side script execution attack targeting other users.
A man-in-the-middle attack requires an attacker to intercept network communications between two parties, which is a network-level interception attack distinct from injecting scripts into a web application's output.
Cross-site scripting (XSS) occurs when an attacker injects malicious JavaScript or other client-side code into web content - often via an input field or URL parameter - that is later rendered and executed by another user's browser. It exploits the browser's trust in content served from a legitimate site, and is caused by applications failing to properly validate input and encode output before rendering it as HTML, as defined by OWASP.
Concept tested: OWASP Top 10 cross-site scripting (XSS) identification
Source: https://owasp.org/www-community/attacks/xss/
Topics
Community Discussion
No community discussion yet for this question.