
1Z0-062 · Question #85
You are connected using SQL* Plus to a multitenant container database (CDB) with SYSDBA privileges and execute the following sequence statements: What is the result of the last SET CONTAINER…
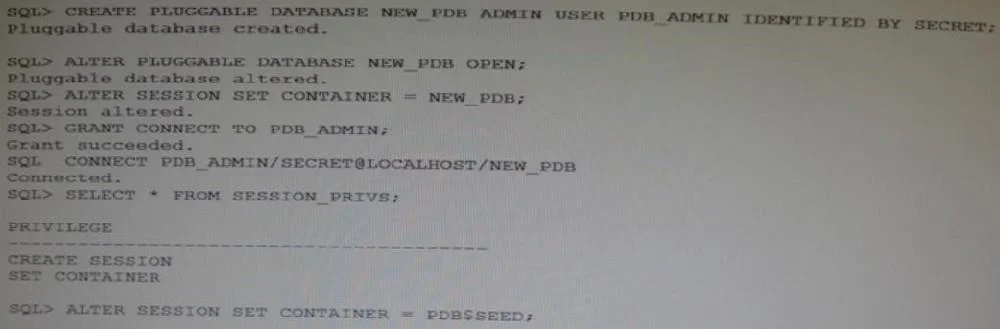
The correct answer is C. It fails because local users are unable to use the SET CONTAINER statement. The SET CONTAINER statement requires the executing user to be a common user with the SET CONTAINER privilege. Local users are scoped to a single PDB and lack the CDB-level authority to switch containers.
Question
You are connected using SQL* Plus to a multitenant container database (CDB) with SYSDBA privileges and execute the following sequence statements:
What is the result of the last SET CONTAINER statement and why is it so?
Exhibit
Options
- AIt succeeds because the PDB_ADMIN user has the required privileges.
- BIt fails because common users are unable to use the SET CONTAINER statement.
- CIt fails because local users are unable to use the SET CONTAINER statement.
- DIf fails because the SET CONTAINER statement cannot be used with PDB$SEED as the target
How the community answered
(58 responses)- A5% (3)
- B19% (11)
- C67% (39)
- D9% (5)
Why each option
The SET CONTAINER statement requires the executing user to be a common user with the SET CONTAINER privilege. Local users are scoped to a single PDB and lack the CDB-level authority to switch containers.
PDB_ADMIN cannot have the required privileges for SET CONTAINER because it is a local user; the SET CONTAINER privilege is only meaningful and grantable in a cross-container context available to common users.
Common users are not restricted from using SET CONTAINER; a common user granted the SET CONTAINER privilege WITH ADMIN OPTION can successfully switch between containers, so the restriction applies specifically to local users.
PDB_ADMIN is a local user created within a specific PDB, meaning its scope is limited to that PDB and it has no visibility or authority at the CDB root level. The SET CONTAINER statement requires a common user (one created in the root container, typically with the C## prefix) granted the SET CONTAINER privilege, because only common users have multi-container scope. Since local users cannot cross container boundaries, the statement fails regardless of what privileges have been granted locally.
The target of SET CONTAINER being PDB$SEED is not the reason for the failure; PDB$SEED is a valid target for the statement - the failure is caused by the user type (local), not the destination container.
Concept tested: Oracle Multitenant SET CONTAINER privilege and local vs common user scope
Source: https://docs.oracle.com/en/database/oracle/oracle-database/12.2/dbseg/managing-security-for-oracle-database-users.html#GUID-3B0E1A38-8CA8-4CB5-A6F3-75C2ACD55B17
Topics
Community Discussion
No community discussion yet for this question.