
SY0-701 · Question #311
A security analyst finds a rogue device during a monthly audit of current endpoint assets that are connected to the network. The corporate network utilizes 002.1X for access control. To be allowed…
The correct answer is A. A user performed a MAC cloning attack with a personal device. The most likely way a rogue device was able to connect to the network is through a MAC cloning attack. In this attack, a personal device copies the MAC address of an authorized device, bypassing the 802.1X access control that relies on known hardware addresses for network…
Question
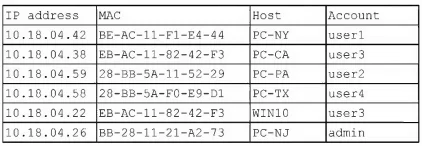
A security analyst finds a rogue device during a monthly audit of current endpoint assets that are connected to the network. The corporate network utilizes 002.1X for access control. To be allowed on the network, a device must have a Known hardware address, and a valid user name and password must be entered in a captive portal. The following is the audit report:
Which of the following is the most likely way a rogue device was allowed to connect?
Exhibit
Options
- AA user performed a MAC cloning attack with a personal device.
- BA DMCP failure caused an incorrect IP address to be distributed
- CAn administrator bypassed the security controls for testing.
- DDNS hijacking let an attacker intercept the captive portal traffic.
How the community answered
(17 responses)- A59% (10)
- B12% (2)
- C24% (4)
- D6% (1)
Explanation
The most likely way a rogue device was able to connect to the network is through a MAC cloning attack. In this attack, a personal device copies the MAC address of an authorized device, bypassing the 802.1X access control that relies on known hardware addresses for network access. The matching MAC addresses in the audit report suggest that this technique was used to gain unauthorized network access.
Community Discussion
No community discussion yet for this question.