
SY0-701 · Question #293
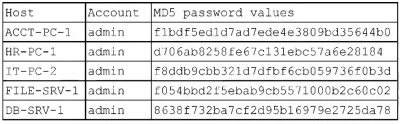
A security administrator recently reset local passwords and the following values were recorded in the system: Which of the following in the security administrator most likely protecting against?
The correct answer is C. Pass-the-hash attacks. The scenario shows MD5 hashed password values. The most likely reason the security administrator is focusing on these values is to protect against pass-the-hash attacks. In this type of attack, an attacker can use a captured hash to authenticate without needing to know the…
Question
A security administrator recently reset local passwords and the following values were recorded in the system:
Which of the following in the security administrator most likely protecting against?
Exhibit
Options
- AAccount sharing
- BWeak password complexity
- CPass-the-hash attacks
- DPassword compromise
How the community answered
(35 responses)- A9% (3)
- B31% (11)
- C43% (15)
- D17% (6)
Explanation
The scenario shows MD5 hashed password values. The most likely reason the security administrator is focusing on these values is to protect against pass-the-hash attacks. In this type of attack, an attacker can use a captured hash to authenticate without needing to know the actual plaintext password. By managing and monitoring these hashes, the administrator can implement strategies to mitigate this type of threat.
Community Discussion
No community discussion yet for this question.