
SY0-701 · Question #1017
SIMULATION 5 vulnerabilities exist, such as directory traversals, cross-site scripting, cross-site forgery, and insecure protocols. You are tasked with reducing the attack space and enabling secure…
This task aims to reduce the attack space and enable secure protocols for a web architecture vulnerable to common exploits like directory traversals, cross-site scripting, and insecure protocols.
Question
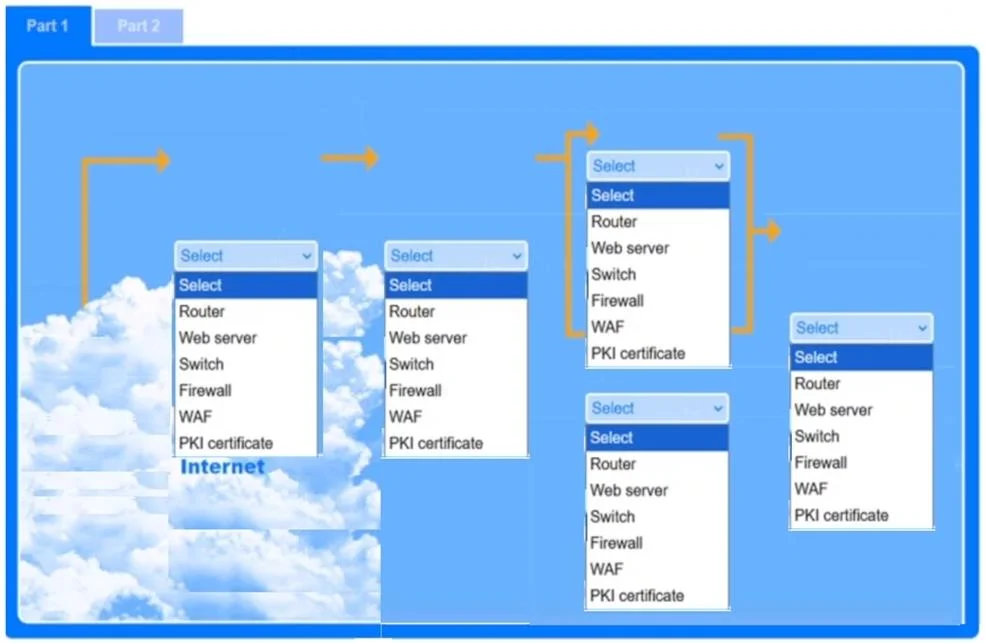
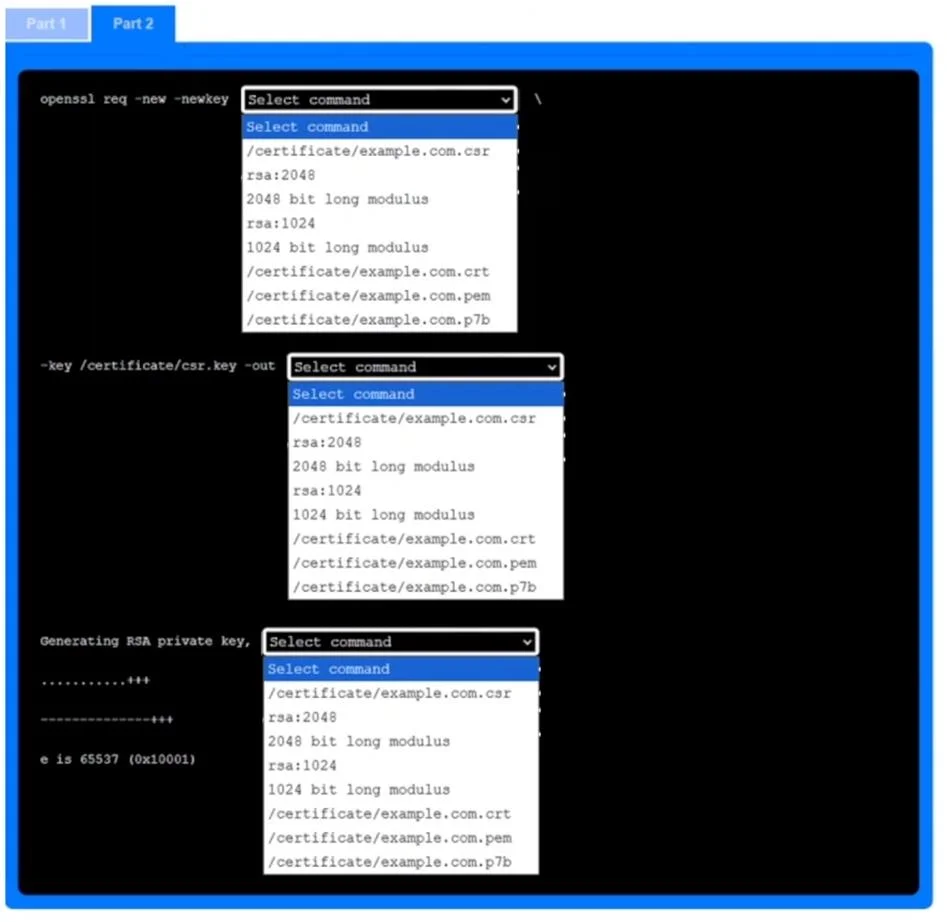
SIMULATION 5 vulnerabilities exist, such as directory traversals, cross-site scripting, cross-site forgery, and insecure protocols. You are tasked with reducing the attack space and enabling secure protocols. INSTRUCTIONS Part 1 Use the drop-down menus to select the appropriate technologies tor each location to implement a secure and resilient web architecture Not all technologies will be used, and technologies may be used multiple times. Part 2 Use the drop-down menus to select the appropriate command snippets from the drop-down menus. Each command section must be filled. If at any time you would like to bring back the initial state of the simulation, please click the Reset All button. Answer:
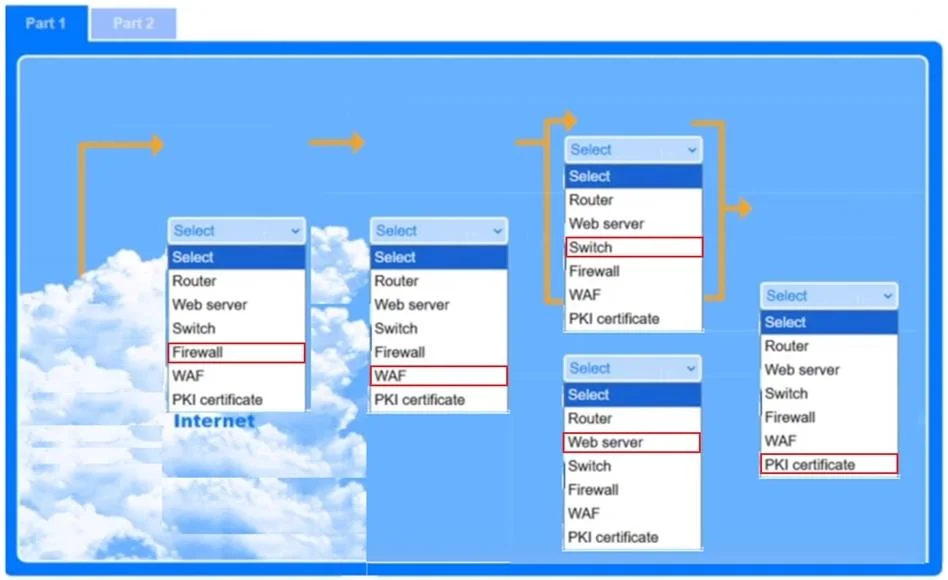
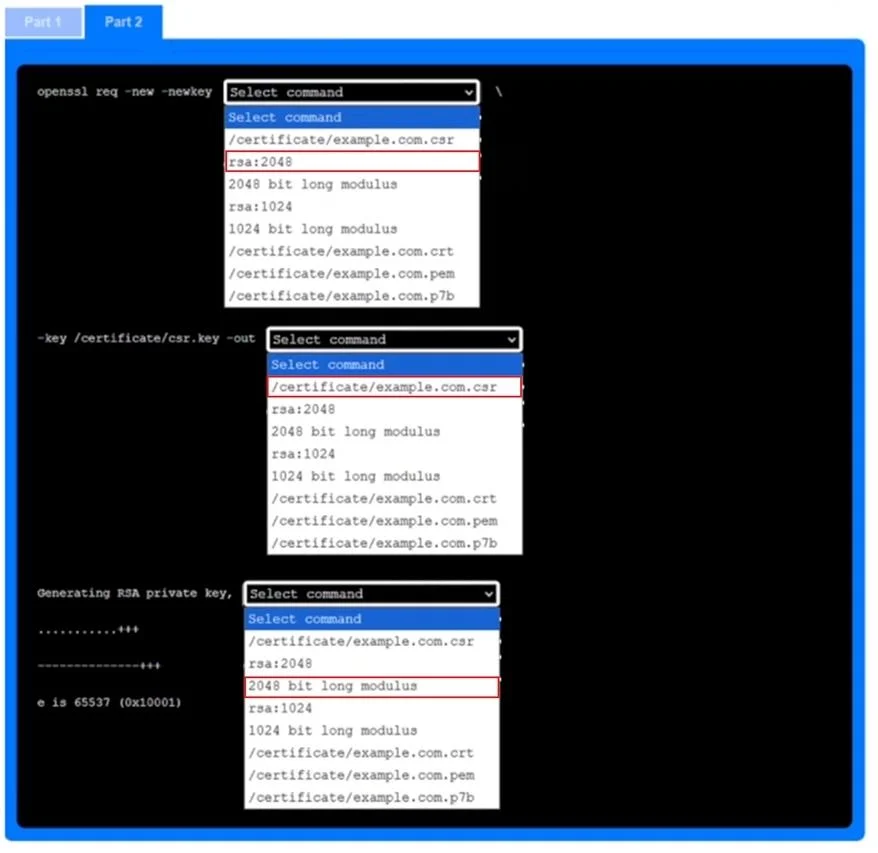
Part 1 A firewall is placed at the edge to filter unwanted or malicious traffic from the Internet before it reaches internal resources. A WAF specifically protects against web-based attacks like XSS, CSRF, and directory traversal by filtering and monitoring HTTP traffic. A switch is used for internal network segmentation and connecting devices within the secure network. The web server hosts the application and should be placed behind security controls for protection. A PKI certificate enables HTTPS, ensuring encrypted and secure communication to mitigate insecure protocol risks. Part 2 rsa:2048 – Generates a 2048-bit RSA key pair, providing modern, recommended key strength. /certificate/example.com.csr – Saves the certificate-signing request that will be sent to a CA. 2048 bit long modulus – Confirms the key was generated with the intended 2048-bit length, validating the command sequence.
Exhibits
Explanation
This task aims to reduce the attack space and enable secure protocols for a web architecture vulnerable to common exploits like directory traversals, cross-site scripting, and insecure protocols.
Concept tested. Web security architecture, attack surface reduction, secure protocols
Reference. https://docs.aws.amazon.com/waf/latest/developerguide/waf-overview.html
Community Discussion
No community discussion yet for this question.