
SY0-501 · Question #332
A company's AUP requires: - Passwords must meet complexity requirements. - Passwords are changed at least once every six months. - Passwords must be at least eight characters long. An auditor is…
The correct answer is C. Password expiration. The AUP mandates passwords be changed at least every six months, but the audit report reveals this policy is not being enforced technically. The auditor must recommend the control that directly enforces mandatory password rotation.
Question
A company's AUP requires:
- Passwords must meet complexity requirements.
- Passwords are changed at least once every six months.
- Passwords must be at least eight characters long.
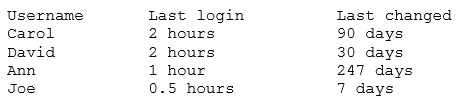
An auditor is reviewing the following report:
Which of the following controls should the auditor recommend to enforce the AUP?
Exhibit
Options
- AAccount lockout thresholds
- BAccount recovery
- CPassword expiration
- DProhibit password reuse
How the community answered
(33 responses)- A6% (2)
- B3% (1)
- C79% (26)
- D12% (4)
Why each option
The AUP mandates passwords be changed at least every six months, but the audit report reveals this policy is not being enforced technically. The auditor must recommend the control that directly enforces mandatory password rotation.
Account lockout thresholds control how many failed login attempts are permitted before an account is locked, which addresses brute-force protection but does not enforce periodic password changes.
Account recovery defines the process for regaining access to a locked or compromised account and does not address the requirement for passwords to be changed on a scheduled basis.
Password expiration is the technical control that forces users to change their passwords after a defined maximum period - in this case, every six months (180 days). Without configuring password expiration in the identity/directory system, the AUP requirement for periodic password changes cannot be automatically enforced, leaving it as an unenforced policy rather than a technical control.
Prohibiting password reuse prevents users from cycling back to previously used passwords, which is a complementary control but does not enforce the six-month mandatory change interval identified as missing in the audit.
Concept tested: Enforcing periodic password changes via expiration policy
Source: https://learn.microsoft.com/en-us/microsoft-365/admin/misc/password-policy-recommendations?view=o365-worldwide
Topics
Community Discussion
No community discussion yet for this question.