
SSCP · Question #282
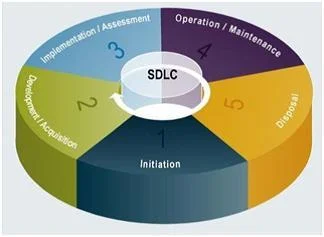
During which phase of an IT system life cycle are security requirements developed?
The correct answer is C. Functional design analysis and Planning. Security requirements are formally developed during the Functional Design Analysis and Planning phase, where system requirements - including security needs - are identified, analyzed, and documented before any implementation begins. Building security in at the design stage is a…
Question
Exhibit
Options
- AOperation
- BInitiation
- CFunctional design analysis and Planning
- DImplementation
How the community answered
(34 responses)- B3% (1)
- C94% (32)
- D3% (1)
Explanation
Security requirements are formally developed during the Functional Design Analysis and Planning phase, where system requirements - including security needs - are identified, analyzed, and documented before any implementation begins. Building security in at the design stage is a core principle ('security by design'). The Initiation phase (B) identifies the need for the system at a high level. Implementation (D) and Operation (A) occur after requirements have already been defined.
Topics
Community Discussion
No community discussion yet for this question.