
SCS-C02 · Question #197
A company wants to deny a specific federated user named Bob access to an Amazon S3 bucket named DOC-EXAMPLE-BUCKET. The company wants to meet this requirement by using a bucket policy. The company…
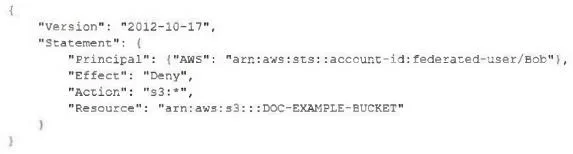
The correct answer is B. { "Version": "2012-10-17", "Statement": [ { "Principal": { "AWS": "arn:aws:sts::account-id:federated-user/Bob" }, "Effect": "Deny", "Action": "s3:*", "Resource": "arn:aws:s3:::DOC-EXAMPLE-BUCKET" } ] }. Option B is correct because it uses a Deny effect with the correct ARN format for a federated user (arn:aws:sts::account-id:federated-user/Bob). An explicit Deny in a bucket policy will override any Allow permissions Bob has for this specific S3 bucket, while leaving all his…
Question
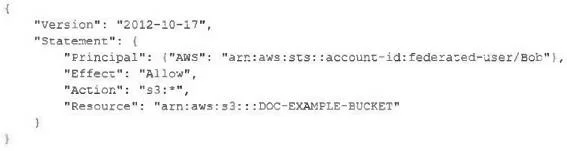
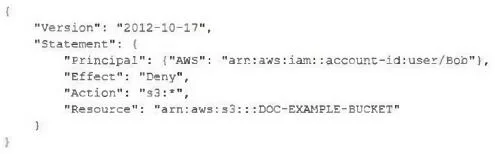
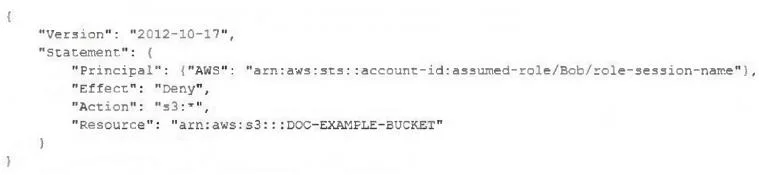
A company wants to deny a specific federated user named Bob access to an Amazon S3 bucket named DOC-EXAMPLE-BUCKET. The company wants to meet this requirement by using a bucket policy. The company also needs to ensure that this bucket policy affects Bob's S3 permissions only. Any other permissions that Bob has must remain intact. Which policy should the company use to meet these requirements? A. B. C. D.
Exhibits
Options
- A{ "Version": "2012-10-17", "Statement": [ { "Principal": { "AWS": "arn:aws:sts::account-id:federated-user/Bob" }, "Effect": "Allow", "Action": "s3:*", "Resource": "arn:aws:s3:::DOC-EXAMPLE-BUCKET" } ] }
- B{ "Version": "2012-10-17", "Statement": [ { "Principal": { "AWS": "arn:aws:sts::account-id:federated-user/Bob" }, "Effect": "Deny", "Action": "s3:*", "Resource": "arn:aws:s3:::DOC-EXAMPLE-BUCKET" } ] }
- C{ "Version": "2012-10-17", "Statement": [ { "Principal": { "AWS": "arn:aws:iam::account-id:user/Bob" }, "Effect": "Deny", "Action": "s3:*", "Resource": "arn:aws:s3:::DOC-EXAMPLE-BUCKET" } ] }
- D{ "Version": "2012-10-17", "Statement": [ { "Principal": { "AWS": "arn:aws:sts::account-id:assumed-role/Bob" }, "Effect": "Deny", "Action": "s3:*", "Resource": "arn:aws:s3:::DOC-EXAMPLE-BUCKET" } ] }
How the community answered
(32 responses)- A16% (5)
- B72% (23)
- C9% (3)
- D3% (1)
Explanation
Option B is correct because it uses a Deny effect with the correct ARN format for a federated user (arn:aws:sts::account-id:federated-user/Bob). An explicit Deny in a bucket policy will override any Allow permissions Bob has for this specific S3 bucket, while leaving all his other permissions (non-S3 or other buckets) completely unaffected. Using Deny in a resource-based policy is the precise way to block access for a specific principal without modifying their identity-based policies.
Topics
Community Discussion
No community discussion yet for this question.