
SC-300 · Question #336
SIMULATION Use the following login credentials as needed: To enter your username, place your cursor in the Sign in box and click on the username below. To enter your password, place your cursor in…
The correct approach uses Microsoft Entra Conditional Access to create a sign-in risk-based policy that enforces MFA when sign-in risk is detected at the 'High' level. By navigating to Protection > Conditional Access, creating a new policy, setting the condition to 'Sign-in…
Question
SIMULATION Use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below. To enter your password, place your cursor in the Enter password box and click on the password below. Microsoft 365 Username:[email protected] Microsoft 365 Password: =1122334455667788 If the Microsoft 365 portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab. The following information is for technical support purposes only:
Lab Instance: 99999999 You need to configure Microsoft Entra Identity Protection to meet the following requirements:
- Require multi-factor authentication (MFA) for any sign-ins at the high risk level.
- Apply the configuration to all users except for Mod Administrator.
To complete this task, sign in to the appropriate admin center. Answer:
Exhibit
Explanation
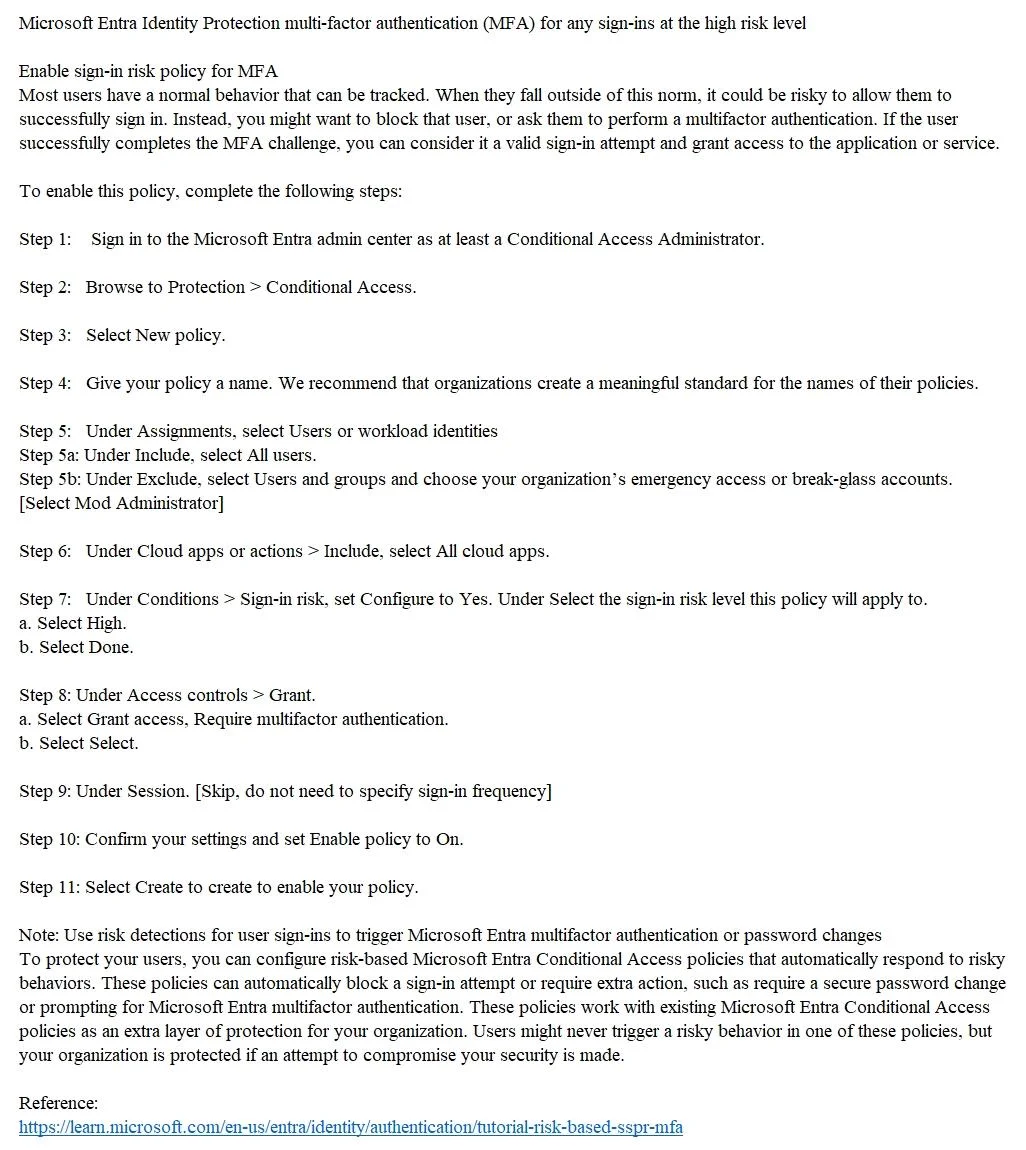
The correct approach uses Microsoft Entra Conditional Access to create a sign-in risk-based policy that enforces MFA when sign-in risk is detected at the 'High' level. By navigating to Protection > Conditional Access, creating a new policy, setting the condition to 'Sign-in risk: High', requiring MFA as the grant control, including 'All users' under assignments, and excluding 'Mod Administrator' specifically, you fulfill both requirements. This method leverages Entra ID Protection's risk signals integrated with Conditional Access, which is the modern and recommended approach for risk-based MFA enforcement.
Topics
Community Discussion
No community discussion yet for this question.