
SC-100 · Question #69
Your company has an Azure subscription that has enhanced security enabled for Microsoft Defender for Cloud. The company signs a contract with the United States government. You need to review the…
The correct answer is B. From Defender for Cloud, add a regulatory compliance standard. Before you can review NIST 800-53 compliance in Microsoft Defender for Cloud, you must first add it as a regulatory compliance standard. NIST 800-53 is not included by default - it must be explicitly added to the Regulatory Compliance dashboard. Only after adding it can you see…
Question
Your company has an Azure subscription that has enhanced security enabled for Microsoft Defender for Cloud. The company signs a contract with the United States government. You need to review the current subscription for NIST 800-53 compliance. What should you do first?
Exhibit
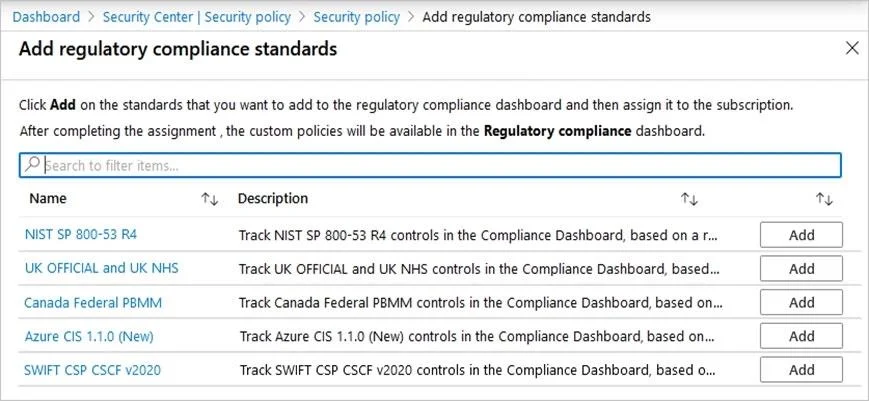
Options
- AFrom Defender for Cloud, review the Azure security baseline for audit report.
- BFrom Defender for Cloud, add a regulatory compliance standard.
- CFrom Defender for Cloud, enable Defender for Cloud plans.
- DFrom Defender for Cloud, review the secure score recommendations.
How the community answered
(39 responses)- A3% (1)
- B79% (31)
- C10% (4)
- D8% (3)
Explanation
Before you can review NIST 800-53 compliance in Microsoft Defender for Cloud, you must first add it as a regulatory compliance standard. NIST 800-53 is not included by default - it must be explicitly added to the Regulatory Compliance dashboard. Only after adding it can you see the controls, assessments, and compliance status. Option A (Azure security baseline) is a different standard. Option C (enabling Defender plans) is a prerequisite for enhanced security but doesn't address NIST 800-53 specifically. Option D (secure score) is a general posture tool, not a compliance-specific report.
Topics
Community Discussion
No community discussion yet for this question.