
PT0-003 · Question #233
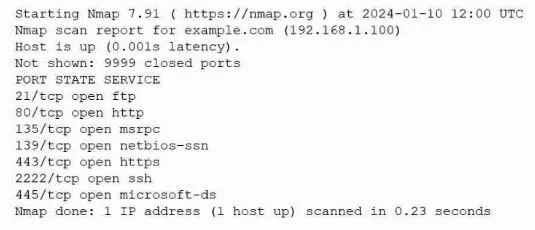
A penetration tester observes the following output from an Nmap command while attempting to troubleshoot connectivity to a Linux server: Which of the following is the most likely reason for the…
The correct answer is A. The SSH service is running on a different port. The key detail in the Nmap scan output is that port 2222/tcp is open and running the SSH service. The standard SSH port is 22, so if the tester was attempting to connect on port 22, they would not succeed because SSH is instead listening on port 2222. This is a common security…
Question
A penetration tester observes the following output from an Nmap command while attempting to troubleshoot connectivity to a Linux server:
Which of the following is the most likely reason for the connectivity issue?
Exhibit
Options
- AThe SSH service is running on a different port.
- BThe SSH service is blocked by a firewall.
- CThe SSH service requires certificate authentication.
- DThe SSH service is not active.
How the community answered
(40 responses)- A75% (30)
- B15% (6)
- C3% (1)
- D8% (3)
Explanation
The key detail in the Nmap scan output is that port 2222/tcp is open and running the SSH service. The standard SSH port is 22, so if the tester was attempting to connect on port 22, they would not succeed because SSH is instead listening on port 2222. This is a common security hardening tactic--moving services to non-standard ports to reduce automated attacks.
Topics
Community Discussion
No community discussion yet for this question.