
PT0-003 · Question #131
SIMULATION You are a penetration tester running port scans on a server. INSTRUCTIONS Part1: Given the output, construct the command that was used to generate this output from the available options…
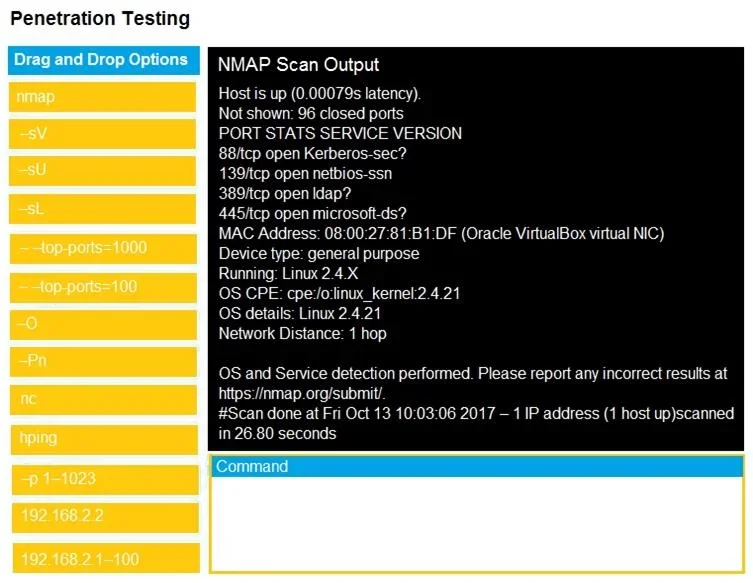
The correct command 'nmap -O -sV 192.168.2.2 --top-ports=100' is accurate because: -O enables OS detection, -sV enables service/version detection (which produces the question marks seen in uncertain service identification), and --top-ports=100 limits the scan to the 100 most…
Question
SIMULATION You are a penetration tester running port scans on a server. INSTRUCTIONS Part1: Given the output, construct the command that was used to generate this output from the available options. Part2: Once the command is appropriately constructed, use the given output to identify the potential attack vectors that should be investigated further. If at any time you would like to bring back the initial state of the simulation, please click the Reset All button. Part1 Part2 Answer:
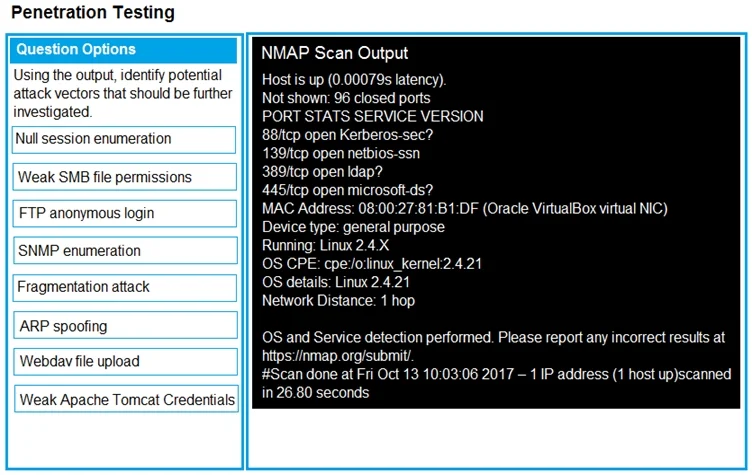
Part 1: nmap -O -sV 192.168.2.2 --top-ports=100 Tried scanning 1 host on my machine. Without -sV you will not get question marks in your port services. We can also clearly see only 100 ports are being scanned. Commander123 is correct. Part 2: Weak SMB file permissions & Null Session Enumeration Because it's obvious port 139 and 445 is open, so that leave SMB vulnerable to weak file permission. This allows for a null session attack to occur.
Exhibits
Explanation
The correct command 'nmap -O -sV 192.168.2.2 --top-ports=100' is accurate because: -O enables OS detection, -sV enables service/version detection (which produces the question marks seen in uncertain service identification), and --top-ports=100 limits the scan to the 100 most common ports as evidenced by the output scope. For Part 2, open ports 139 (NetBIOS) and 445 (SMB) are classic indicators of SMB vulnerability - specifically weak file share permissions and null session enumeration, where an unauthenticated attacker can connect to SMB shares and enumerate users, groups, and shares without credentials.
Topics
Community Discussion
No community discussion yet for this question.