
PT0-002 · Question #95
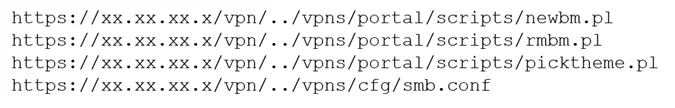
A penetration tester discovered a vulnerability that provides the ability to upload to a path via directory traversal. Some of the files that were discovered through this vulnerability are: Which of…
The correct answer is A. Edit the discovered file with one line of code for remote callback. The SMB.conf file won't give you internal access to the system, it would only be effective for Remote File Inclusion (RFI) which has already been achieved.
Question
A penetration tester discovered a vulnerability that provides the ability to upload to a path via directory traversal. Some of the files that were discovered through this vulnerability are:
Which of the following is the BEST method to help an attacker gain internal access to the affected machine?
Exhibit
Options
- AEdit the discovered file with one line of code for remote callback
- BDownload .pl files and look for usernames and passwords
- CEdit the smb.conf file and upload it to the server
- DDownload the smb.conf file and look at configurations
How the community answered
(52 responses)- A73% (38)
- B15% (8)
- C8% (4)
- D4% (2)
Explanation
The SMB.conf file won't give you internal access to the system, it would only be effective for Remote File Inclusion (RFI) which has already been achieved.
Topics
Community Discussion
No community discussion yet for this question.