
PT0-001 · Question #242
During the exploitation phase of a penetration test, a vulnerability is discovered that allows command execution on a Linux web server. A cursory review confirms the system access is only in a…
The correct answer is A. Only members of the Linux admin group, OPERATORS, ADMINS, jedwards, and operator can. Analyzing the /etc/sudoers file identifies which users and groups can run privileged commands, guiding the tester toward accounts worth compromising for privilege escalation.
Question
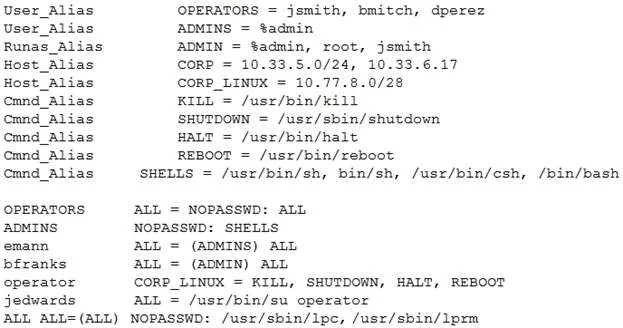
During the exploitation phase of a penetration test, a vulnerability is discovered that allows command execution on a Linux web server. A cursory review confirms the system access is only in a low-privilege user context: www-data. After reviewing, the following output from /etc/sudoers:
Which of the following users should be targeted for privilege escalation?
Exhibit
Options
- AOnly members of the Linux admin group, OPERATORS, ADMINS, jedwards, and operator can
- BAll users on the machine can execute privileged commands useful for privilege escalation.
- CBfranks, emann, members of the Linux admin group, OPERATORS, and ADMINS can execute
- DJedwards, operator, bfranks, emann, OPERATOR, and ADMINS can execute commands useful
How the community answered
(31 responses)- A81% (25)
- B6% (2)
- C10% (3)
- D3% (1)
Why each option
Analyzing the /etc/sudoers file identifies which users and groups can run privileged commands, guiding the tester toward accounts worth compromising for privilege escalation.
The sudoers output, as reflected in the answer choices, limits elevated command execution to specific named users (jedwards, operator) and group members (Linux admin, OPERATORS, ADMINS). Targeting these identities gives the tester a path to escalate from the low-privilege www-data context by pivoting to or impersonating a user who has sudo rights. Users or groups not listed cannot run privileged commands and are therefore lower-value targets for escalation.
A permissive sudoers configuration granting all users privilege escalation rights is not indicated by the described output; the output restricts access to specific users and groups.
This choice omits jedwards and operator, who are explicitly named in the sudoers file and are valid escalation targets alongside the group members.
This choice misidentifies the group name as OPERATOR (singular) rather than OPERATORS and conflates separately listed entries, making it an inaccurate reading of the sudoers output.
Concept tested: Sudoers file analysis for privilege escalation targeting
Source: https://www.sudo.ws/docs/man/sudoers.man/
Topics
Community Discussion
No community discussion yet for this question.