
PCNSE · Question #243
An administrator has created an SSL Decryption policy rule that decrypts SSL sessions on any port. Which log entry can the administrator use to verify that sessions are being decrypted?
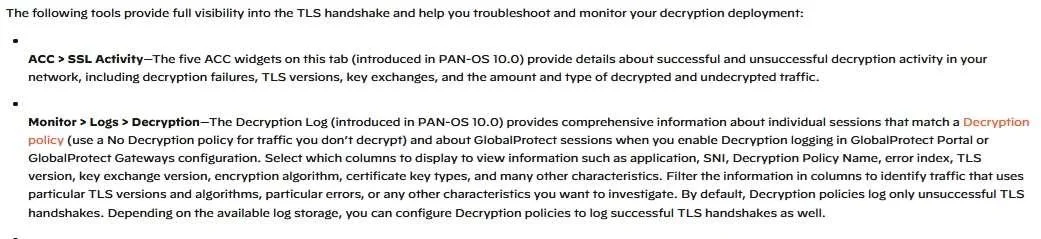
The correct answer is B. Decryption log. The Decryption log (B) is the dedicated log type that records details of SSL/TLS sessions inspected by decryption policy rules, including whether the session was decrypted or bypassed, the policy rule matched, cipher suite used, and certificate details. This is the…
Question
An administrator has created an SSL Decryption policy rule that decrypts SSL sessions on any port. Which log entry can the administrator use to verify that sessions are being decrypted?
Exhibit
Options
- AIn the details of the Traffic log entries
- BDecryption log
- CData Filtering log
- DIn the details of the Threat log entries
How the community answered
(45 responses)- B93% (42)
- C2% (1)
- D4% (2)
Explanation
The Decryption log (B) is the dedicated log type that records details of SSL/TLS sessions inspected by decryption policy rules, including whether the session was decrypted or bypassed, the policy rule matched, cipher suite used, and certificate details. This is the authoritative source to confirm that decryption is functioning. Traffic logs (A) record connection metadata but do not provide decryption-specific detail. Data Filtering logs (C) relate to DLP content inspection. Threat logs (D) record detected threats, not decryption status.
Topics
Community Discussion
No community discussion yet for this question.