
PCNSE · Question #144
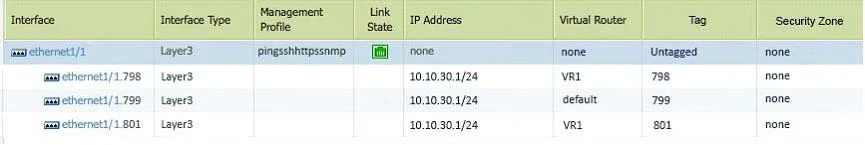
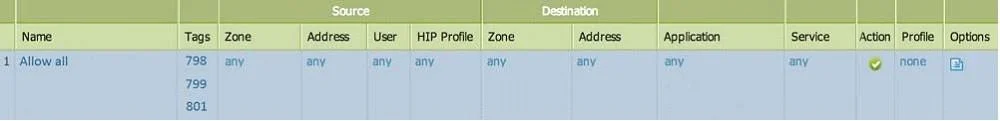
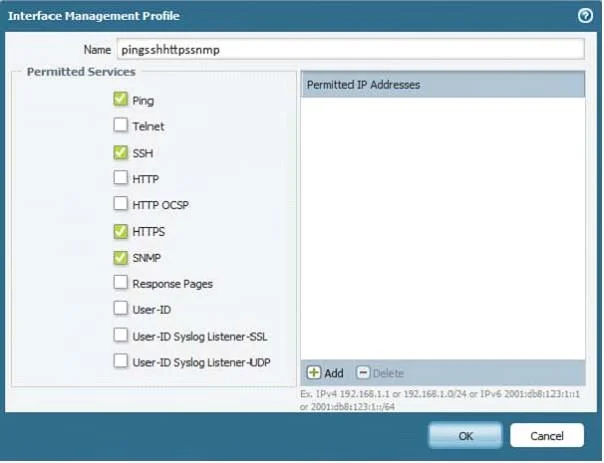
Ethernet1/1 has been configured with the following subinterfaces: The following security policy rule is applied: The Interface Management Profile permits the following: A customer is trying to ping…
The correct answer is A. The ping will not be successful because there is no management profile attached to. The ping from VLAN 799 to 10.10.10.1 will fail because ethernet1/1.799 is configured with IP 10.10.10.1/24, meaning the customer is pinging the firewall's subinterface itself, and the management profile is not attached to this subinterface, thus not allowing ping.
Question
Ethernet1/1 has been configured with the following subinterfaces:
The following security policy rule is applied:
The Interface Management Profile permits the following:
A customer is trying to ping 10.10.10.1 from VLAN 799 IP 10.10.10.2/24. What will be the result of this ping?
Exhibits
Options
- AThe ping will not be successful because there is no management profile attached to
- BThe ping will not successful because the management profile applied to ethernet1/1 allows ping.
- CThe ping will not be successful because the security policy does not apply to VLAN 799.
- DThe ping will not be successful because the virtual router is different from the other subinterfaces.
- EThe ping will not successful because the security policy permits this traffic.
How the community answered
(54 responses)- A83% (45)
- B2% (1)
- C4% (2)
- D2% (1)
- E9% (5)
Why each option
The ping from VLAN 799 to 10.10.10.1 will fail because `ethernet1/1.799` is configured with IP `10.10.10.1/24`, meaning the customer is pinging the firewall's subinterface itself, and the management profile is not attached to this subinterface, thus not allowing ping.
The target IP 10.10.10.1 is the IP address of the `ethernet1/1.799` subinterface itself. For a device to respond to management traffic (like ping) on a data plane interface, an Interface Management Profile permitting ping must be explicitly attached to that specific subinterface; without it, the firewall will not respond to the ping, leading to failure.
The statement is contradictory; if the management profile allows ping and is applied to the correct interface, the ping should be successful.
The security policy is not relevant here for pinging the firewall's *own interface*; Interface Management Profiles control access to the firewall itself, not through-traffic subject to security policies.
All subinterfaces `ethernet1/1.100`, `ethernet1/1.200`, `ethernet1/1.799` are in the "default" virtual router, so routing between them via the firewall is not the issue for a ping directly to the firewall's IP on one of those subinterfaces.
The security policy permits traffic *through* the firewall, but a ping *to* the firewall's interface is controlled by the Interface Management Profile, not the security policy.
Concept tested: Interface management profile and self-generated traffic
Source: https://docs.paloaltonetworks.com/pan-os/11-1/pan-os-admin/network/configure-interface-management-profiles.html
Topics
Community Discussion
No community discussion yet for this question.