
NSE5_SSE_AD-7.6 · Question #21
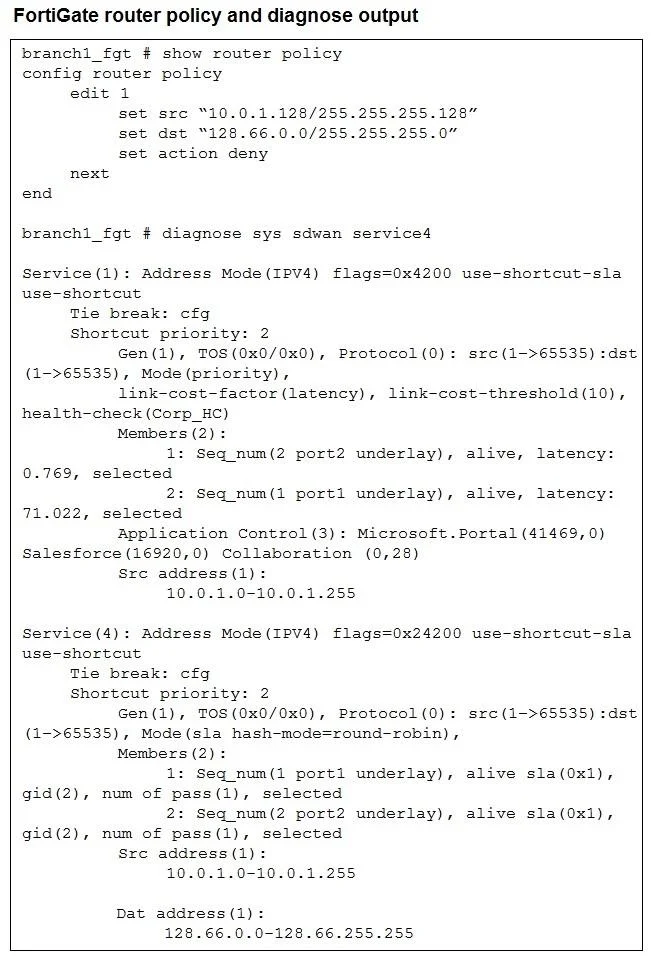
Refer to the exhibit. How does FortiGate handle the traffic with the source IP 10.0.1.130 and the destination IP 128.66.0.125?
The correct answer is B. FortiGate routes the traffic flow according to the FIB. On FortiGate, a policy route (PBR) with action deny does not drop the traffic outright. Instead, it prevents the traffic from being steered by that policy route, and the packet is then handed back to the regular routing lookup (FIB): Source 10.0.1.130 matches 10.0.1.128/25…
Question
Refer to the exhibit. How does FortiGate handle the traffic with the source IP 10.0.1.130 and the destination IP 128.66.0.125?
Exhibits

Options
- AFortiGate steers the traffic flow through port2.
- BFortiGate routes the traffic flow according to the FIB.
- CFortiGate load balances the traffic flow through port1 and port2.
- DFortiGate drops the traffic flow.
How the community answered
(69 responses)- A9% (6)
- B84% (58)
- C1% (1)
- D6% (4)
Explanation
On FortiGate, a policy route (PBR) with action deny does not drop the traffic outright. Instead, it prevents the traffic from being steered by that policy route, and the packet is then handed back to the regular routing lookup (FIB): Source 10.0.1.130 matches 10.0.1.128/25 Destination 128.66.0.125 matches 128.66.0.0/24 Router policy says action deny -> do not use this policy route Result: FortiGate falls back to the FIB (normal routing table).
Topics
Community Discussion
No community discussion yet for this question.