
NSE4 · Question #277
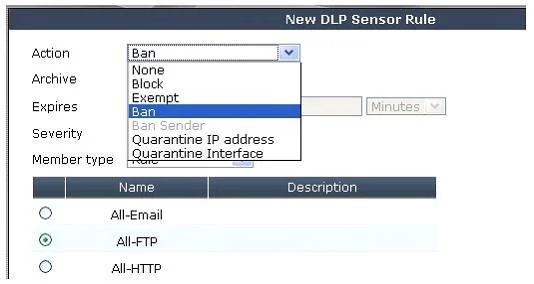
An administrator is configuring a DLP rule for FTP traffic. When adding the rule to a DLP sensor, the administrator notes that the Ban Sender action is not available (greyed-out), as shown in the…
The correct answer is A. The Ban Sender action is never available for FTP traffic. The 'Ban Sender' action in FortiGate DLP is unavailable for FTP traffic because it is an email-specific feature designed to block email senders.
Question
An administrator is configuring a DLP rule for FTP traffic. When adding the rule to a DLP sensor, the administrator notes that the Ban Sender action is not available (greyed-out), as shown in the exhibit. Which of the following is the best explanation for the Ban Sender action NOT being available?
Exhibit
Options
- AThe Ban Sender action is never available for FTP traffic.
- BThe Ban Sender action needs to be enabled globally for FTP traffic on the FortiGate unit before
- CFirewall policy authentication is required before the Ban Sender action becomes available.
- DThe Ban Sender action is only available for known domains. No domains have yet been added to
How the community answered
(40 responses)- A90% (36)
- B5% (2)
- C3% (1)
- D3% (1)
Why each option
The 'Ban Sender' action in FortiGate DLP is unavailable for FTP traffic because it is an email-specific feature designed to block email senders.
The 'Ban Sender' action within FortiGate DLP is exclusively designed for email protocols (like SMTP, POP3, IMAP) to identify and block problematic email addresses. Since FTP is a file transfer protocol and does not involve email senders, this action is technically irrelevant and therefore never available for FTP DLP rules.
There is no global setting on a FortiGate to enable the 'Ban Sender' action for FTP traffic, as the feature is not designed for that protocol.
Firewall policy authentication does not govern the availability of specific DLP actions; rather, it controls user access, while DLP actions are protocol-specific.
The 'Ban Sender' action targets email addresses, not general domains, and its availability is not contingent on pre-adding domains to the FortiGate for FTP traffic.
Concept tested: FortiGate DLP 'Ban Sender' action applicability
Source: https://docs.fortinet.com/document/fortigate/7.4.0/administration-guide/604515/data-leak-prevention
Topics
Community Discussion
No community discussion yet for this question.