
MS-900 · Question #329
Hotspot Question Instructions: For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point. Answer:
The correct answer is Microsoft Service Trust Portal provides audit reports. = Yes; Microsoft Service Trust Portal provides penetration test reports. = Yes; Microsoft Service Trust Portal allows for the configuration of conditional access policies. = No. This hotspot question assesses understanding of the Microsoft Service Trust Portal's capabilities, specifically its role in providing compliance documentation and audit reports versus its inability to configure security policies.
Question
Exhibit
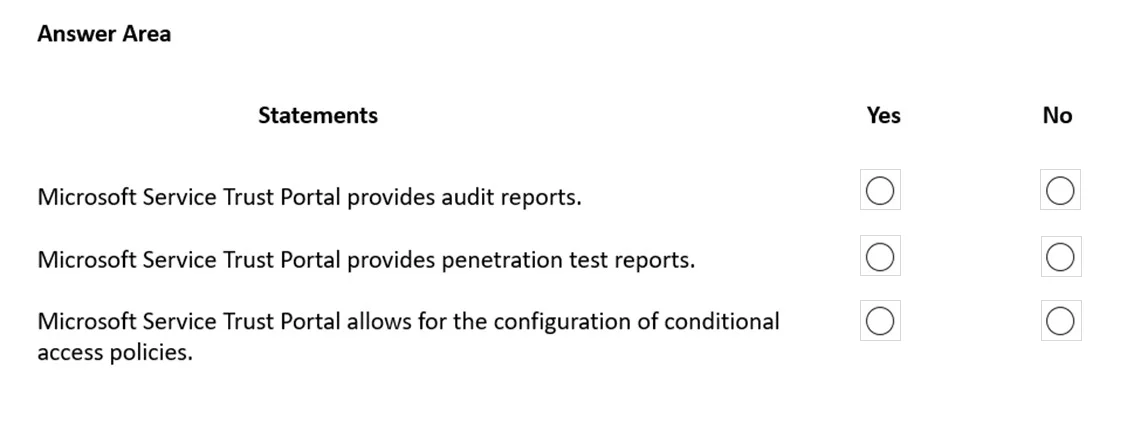
Answer Area
- Microsoft Service Trust Portal provides audit reports.Yes
- Microsoft Service Trust Portal provides penetration test reports.Yes
- Microsoft Service Trust Portal allows for the configuration of conditional access policies.No
Explanation
This hotspot question assesses understanding of the Microsoft Service Trust Portal's capabilities, specifically its role in providing compliance documentation and audit reports versus its inability to configure security policies.
Approach. The correct interaction requires selecting 'Yes' for the first two statements and 'No' for the third statement, based on the functionalities of the Microsoft Service Trust Portal:
-
'Microsoft Service Trust Portal provides audit reports.' - Select Yes. The Microsoft Service Trust Portal (STP) serves as a central repository where customers can access various audit reports (e.g., SOC, ISO, HIPAA, GDPR) that Microsoft produces for its cloud services. These reports help organizations meet their own compliance obligations.
-
'Microsoft Service Trust Portal provides penetration test reports.' - Select Yes. The STP also provides access to detailed penetration test reports conducted by Microsoft on its cloud infrastructure and services. These reports offer insights into the security measures and testing methodologies employed by Microsoft.
-
'Microsoft Service Trust Portal allows for the configuration of conditional access policies.' - Select No. Conditional Access policies are a feature of Azure Active Directory (now Microsoft Entra ID) used to enforce access controls based on conditions such as user location, device state, application, and risk. These policies are configured within the Azure portal or Microsoft Entra admin center, not within the read-only Service Trust Portal, which is primarily for documentation and reports.
Common mistakes.
- common_mistake. A common mistake is confusing the Service Trust Portal with other administrative or security configuration portals within Azure or Microsoft 365. For example, selecting 'Yes' for the third statement would indicate a misunderstanding of the STP's read-only, informational purpose versus the active configuration capabilities found in portals like the Azure portal or Entra admin center. Conversely, selecting 'No' for the first two statements would show a lack of awareness regarding the fundamental purpose of the STP as a resource for compliance and security documentation, including audit and penetration test reports.
Concept tested. The core concept being tested is the understanding of the Microsoft Service Trust Portal's purpose and specific capabilities. This includes knowing what types of compliance and security documentation (like audit reports and penetration test reports) it provides and, crucially, what it does not do (e.g., configure security policies like Conditional Access).
Reference. https://learn.microsoft.com/en-us/microsoft-365/compliance/trust-portal-overview
Topics
Community Discussion
No community discussion yet for this question.