
DP-203 · Question #155
Drag and Drop Question You have an Azure Synapse Analytics SQL pool named Pool1 on a logical Microsoft SQL server named Server1. You need to implement Transparent Data Encryption (TDE) on Pool1 by…
The correct answer is Assign a managed identity to Server1.; Create an Azure key vault and grant the managed identity permissions to the key vault.; Add key1 to the Azure key vault.; Configure key1 as the TDE protector for Server1.; Enable TDE on Pool1. The correct sequence follows the logical dependency chain for implementing customer-managed TDE: first, Server1 needs a managed identity so it can authenticate to Azure Key Vault; next, the Key Vault must be created and the managed identity granted appropriate permissions (Get…
Question
Exhibit
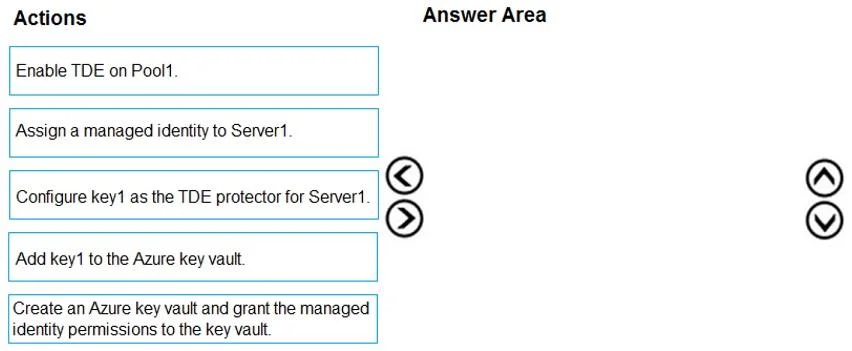
Answer Area
Drag items
Correct arrangement
- Assign a managed identity to Server1.
- Create an Azure key vault and grant the managed identity permissions to the key vault.
- Add key1 to the Azure key vault.
- Configure key1 as the TDE protector for Server1.
- Enable TDE on Pool1.
Explanation
The correct sequence follows the logical dependency chain for implementing customer-managed TDE: first, Server1 needs a managed identity so it can authenticate to Azure Key Vault; next, the Key Vault must be created and the managed identity granted appropriate permissions (Get, WrapKey, UnwrapKey); then key1 is added to the Key Vault; key1 is designated as the TDE protector for Server1 so the server knows which key to use for encryption; and finally TDE is enabled on Pool1 to activate encryption using that protector. Each step is a prerequisite for the next - you cannot configure a TDE protector before the key exists in Key Vault, and you cannot enable TDE with a customer key before the protector is set.
Topics
Community Discussion
No community discussion yet for this question.