
CS0-003 · Question #359
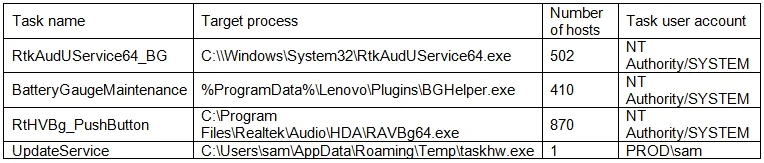
A threat hunter seeks to identify new persistence mechanisms installed in an organization's environment. In collecting scheduled tasks from all enterprise workstations, the following host details…
The correct answer is C. Perform a public search for malware reports on the taskhw.exe. The first step should be to perform a public search for malware reports on taskhw.exe, as this file is suspicious for several reasons: it is located in a non-standard path, it has a high CPU usage, it is signed by an unknown entity, and it is only present on one host. A public…
Question
A threat hunter seeks to identify new persistence mechanisms installed in an organization's environment. In collecting scheduled tasks from all enterprise workstations, the following host details are aggregated:
Which of the following actions should the hunter perform first based on the details above?
Exhibit
Options
- AAcquire a copy of taskhw.exe from the impacted host.
- BScan the enterprise to identify other systems with taskhdw.exe present.
- CPerform a public search for malware reports on the taskhw.exe.
- DChange the account that runs the taskhw.exe scheduled task.
How the community answered
(42 responses)- A10% (4)
- B5% (2)
- C67% (28)
- D19% (8)
Explanation
The first step should be to perform a public search for malware reports on taskhw.exe, as this file is suspicious for several reasons: it is located in a non-standard path, it has a high CPU usage, it is signed by an unknown entity, and it is only present on one host. A public search can help to determine if this file is a known malware or a legitimate program. If it is malware, the hunter can then take appropriate actions to remove it and prevent further damage. The other options are either premature or ineffective, as they do not provide enough information to assess the threat level of taskhw.exe.
Topics
Community Discussion
No community discussion yet for this question.