
CS0-003 · Question #330
A security analyst received an alert regarding multiple successful MFA log-ins for a particular user. When reviewing the authentication logs, the analyst sees the following: Which of the following…
The correct answer is B. Push phishing C. Impossible geo-velocity. Impossible geo-velocity: This is an event where a single user's account is accessed from different geographical locations within a timeframe that is impossible for normal human travel. In the log, we can see that the user "jdoe" is accessing from the United States and then…
Question
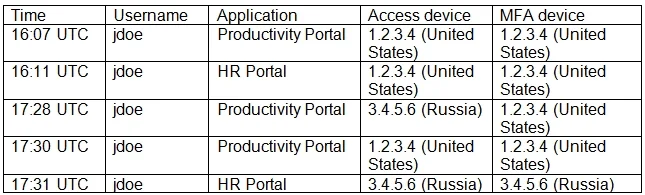
A security analyst received an alert regarding multiple successful MFA log-ins for a particular user. When reviewing the authentication logs, the analyst sees the following:
Which of the following are most likely occurring, base on the MFA logs? (Choose two.)
Exhibit
Options
- ADictionary attack
- BPush phishing
- CImpossible geo-velocity
- DSubscriber identity module swapping
- ERogue access point
- FPassword spray
How the community answered
(25 responses)- A4% (1)
- B52% (13)
- D12% (3)
- E24% (6)
- F8% (2)
Explanation
Impossible geo-velocity: This is an event where a single user's account is accessed from different geographical locations within a timeframe that is impossible for normal human travel. In the log, we can see that the user "jdoe" is accessing from the United States and then within a few minutes from Russia, which is practically impossible to achieve without the use of some form of automated system or if the account credentials are being used by different individuals in different Push phishing: This could also be an indication of push phishing, where the user is tricked into approving a multi-factor authentication request that they did not initiate. This is less clear from the logs directly, but it could be inferred if the user is receiving MFA requests that they are not initiating and are being approved without their genuine desire to access the resources.
Topics
Community Discussion
No community discussion yet for this question.