
CS0-003 · Question #290
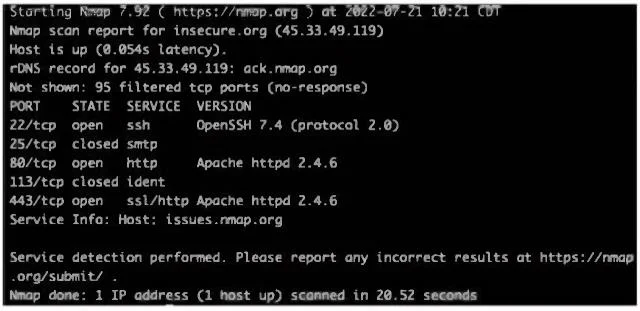
An analyst investigated a website and produced the following: Which of the following syntaxes did the analyst use to discover the application versions on this vulnerable website?
The correct answer is C. nmap -sV -T4 -F insecure.org. The analyst used the command nmap -sV -T4 -F insecure.org to discover the application versions on the vulnerable website. The -sV option in Nmap is used to perform version detection, which identifies the versions of the services running on open ports. The -T4 option sets the…
Question
An analyst investigated a website and produced the following:
Which of the following syntaxes did the analyst use to discover the application versions on this vulnerable website?
Exhibit
Options
- Anmap -sS -T4 -F insecure.org
- Bnmap -C insecure.org
- Cnmap -sV -T4 -F insecure.org
- Dnmap -A insecure.org
How the community answered
(46 responses)- B4% (2)
- C93% (43)
- D2% (1)
Explanation
The analyst used the command nmap -sV -T4 -F insecure.org to discover the application versions on the vulnerable website. The -sV option in Nmap is used to perform version detection, which identifies the versions of the services running on open ports. The -T4 option sets the timing template for faster execution, and -F scans only the most common ports.
Topics
Community Discussion
No community discussion yet for this question.