
CS0-003 · Question #287
A security analyst is trying to validate the results of a web application scan with Burp Suite. The security analyst performs the following: Which of the following vulnerabilities is the security…
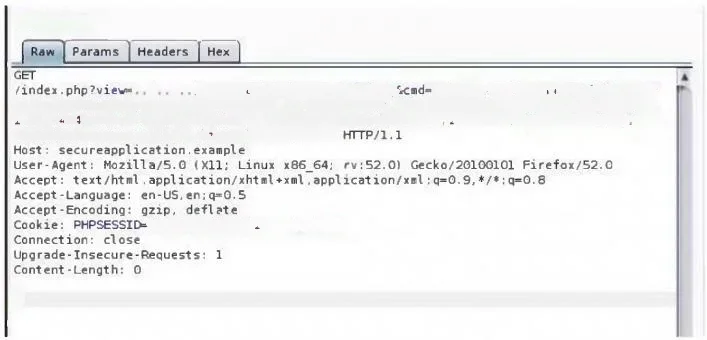
The correct answer is B. LFI. The security analyst is validating a Local File Inclusion (LFI) vulnerability, as indicated by the "/.../.../.../" in the GET request which is a common indicator of directory traversal attempts associated with LFI. The other options are not relevant for this purpose: SQL…
Question
A security analyst is trying to validate the results of a web application scan with Burp Suite. The security analyst performs the following:
Which of the following vulnerabilities is the security analyst trying to validate?
Exhibit
Options
- ASQL injection
- BLFI
- CXSS
- DCSRF
How the community answered
(59 responses)- A14% (8)
- B76% (45)
- C3% (2)
- D7% (4)
Explanation
The security analyst is validating a Local File Inclusion (LFI) vulnerability, as indicated by the "/.../.../.../" in the GET request which is a common indicator of directory traversal attempts associated with LFI. The other options are not relevant for this purpose: SQL injection involves injecting malicious SQL statements into a database query; XSS involves injecting malicious scripts into a web page; CSRF involves tricking a user into performing an unwanted action on a web application.
Topics
Community Discussion
No community discussion yet for this question.