
CS0-003 · Question #272
A penetration tester is conducting a test on an organization's software development website. The penetration tester sends the following request to the web interface: Which of the following exploits…
The correct answer is A. SQL injection. SQL injection is a type of attack that injects malicious SQL statements into a web application's input fields or parameters, in order to manipulate or access the underlying database. The request shown in the image contains an SQL injection attempt, as indicated by the "UNION…
Question
A penetration tester is conducting a test on an organization's software development website. The penetration tester sends the following request to the web interface:
Which of the following exploits is most likely being attempted?
Exhibit
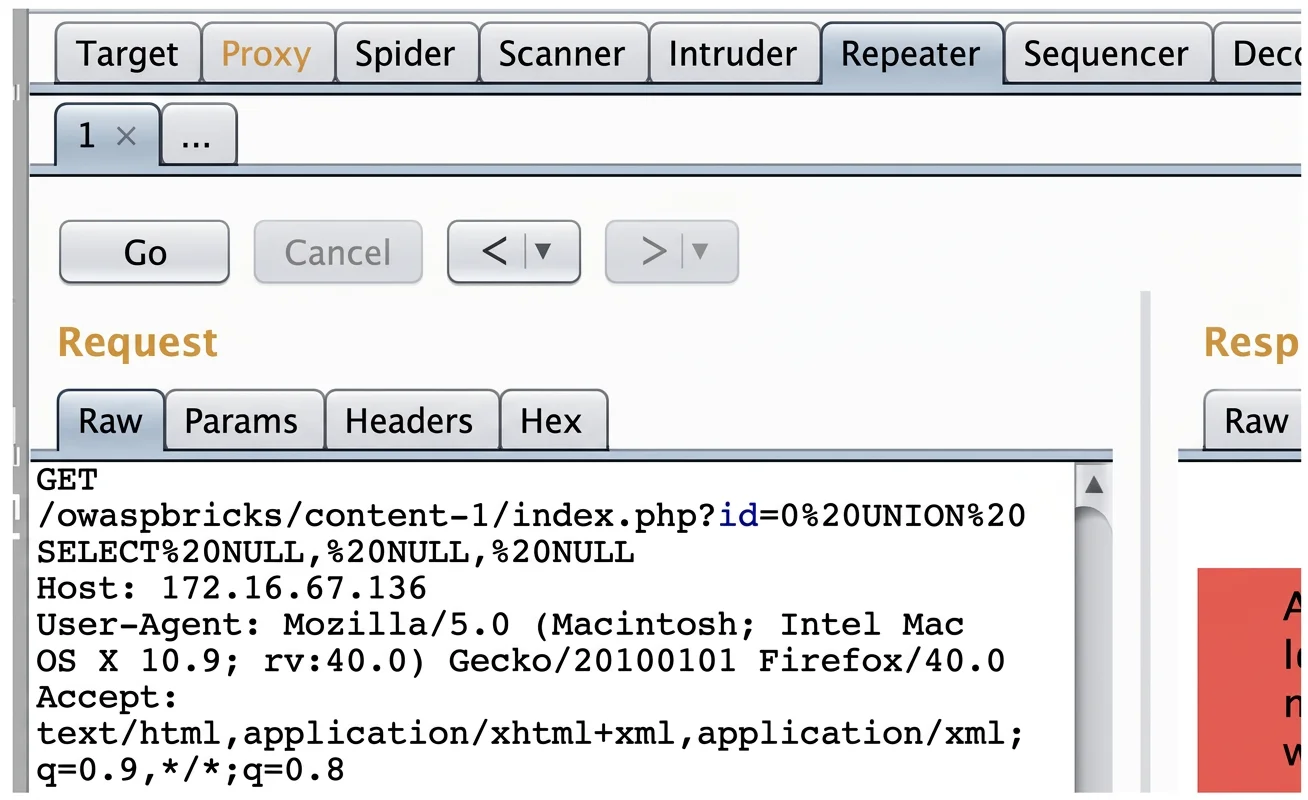
Options
- ASQL injection
- BLocal file inclusion
- CCross-site scripting
- DDirectory traversal
How the community answered
(21 responses)- A76% (16)
- B5% (1)
- C5% (1)
- D14% (3)
Explanation
SQL injection is a type of attack that injects malicious SQL statements into a web application's input fields or parameters, in order to manipulate or access the underlying database. The request shown in the image contains an SQL injection attempt, as indicated by the "UNION SELECT" statement, which is used to combine the results of two or more queries. The attacker is trying to extract information from the database by appending the malicious query to the original one.
Topics
Community Discussion
No community discussion yet for this question.