
CS0-003 · Question #240
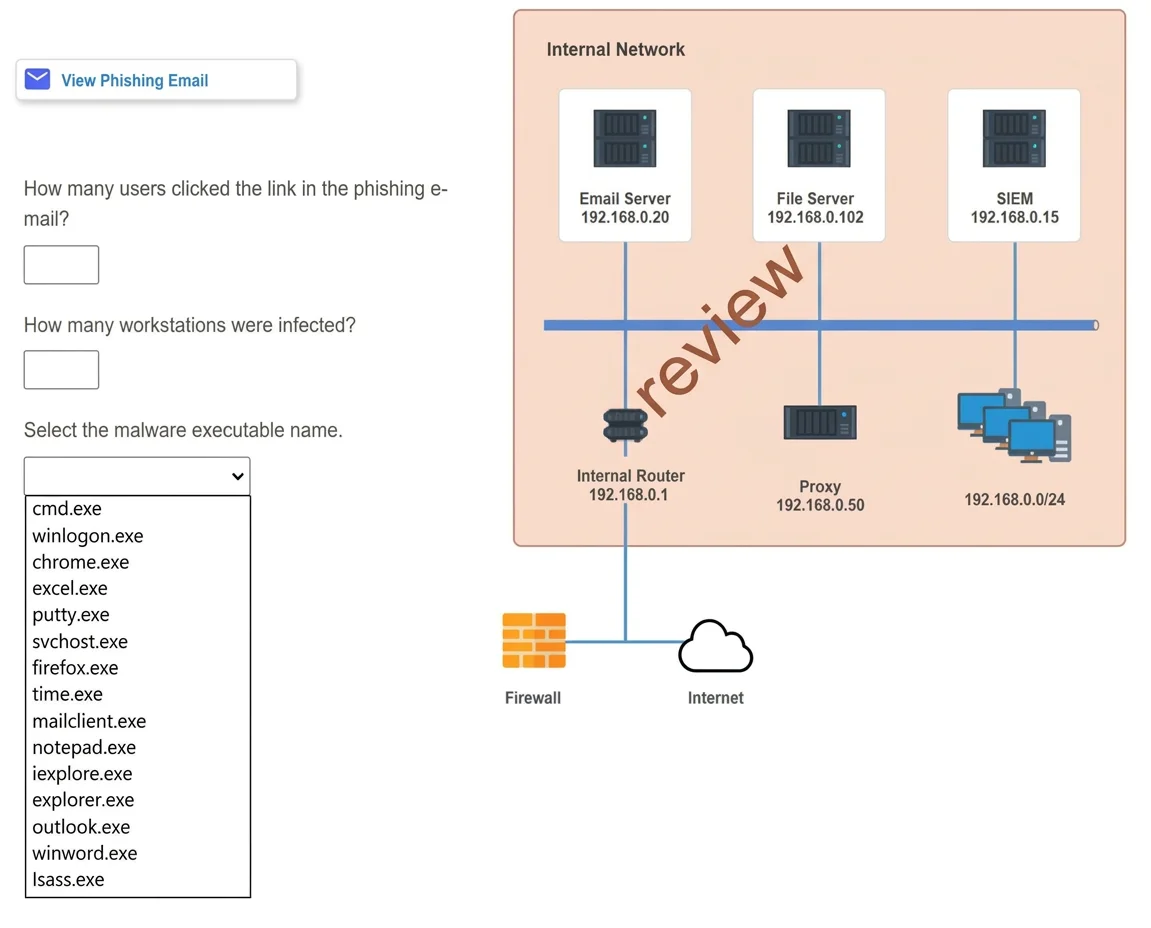
SIMULATION Approximately 100 employees at your company have received a phishing email. As a security analyst, you have been tasked with handling this situation. INSTRUCTIONS Review the information…
This is a simulation-based question from the CompTIA Security+ exam that requires candidates to analyze log files, email headers, endpoint detection reports, or SIEM data to extract specific incident response metrics. The correct answers are derived by carefully reviewing the…
Question
Exhibits
Explanation
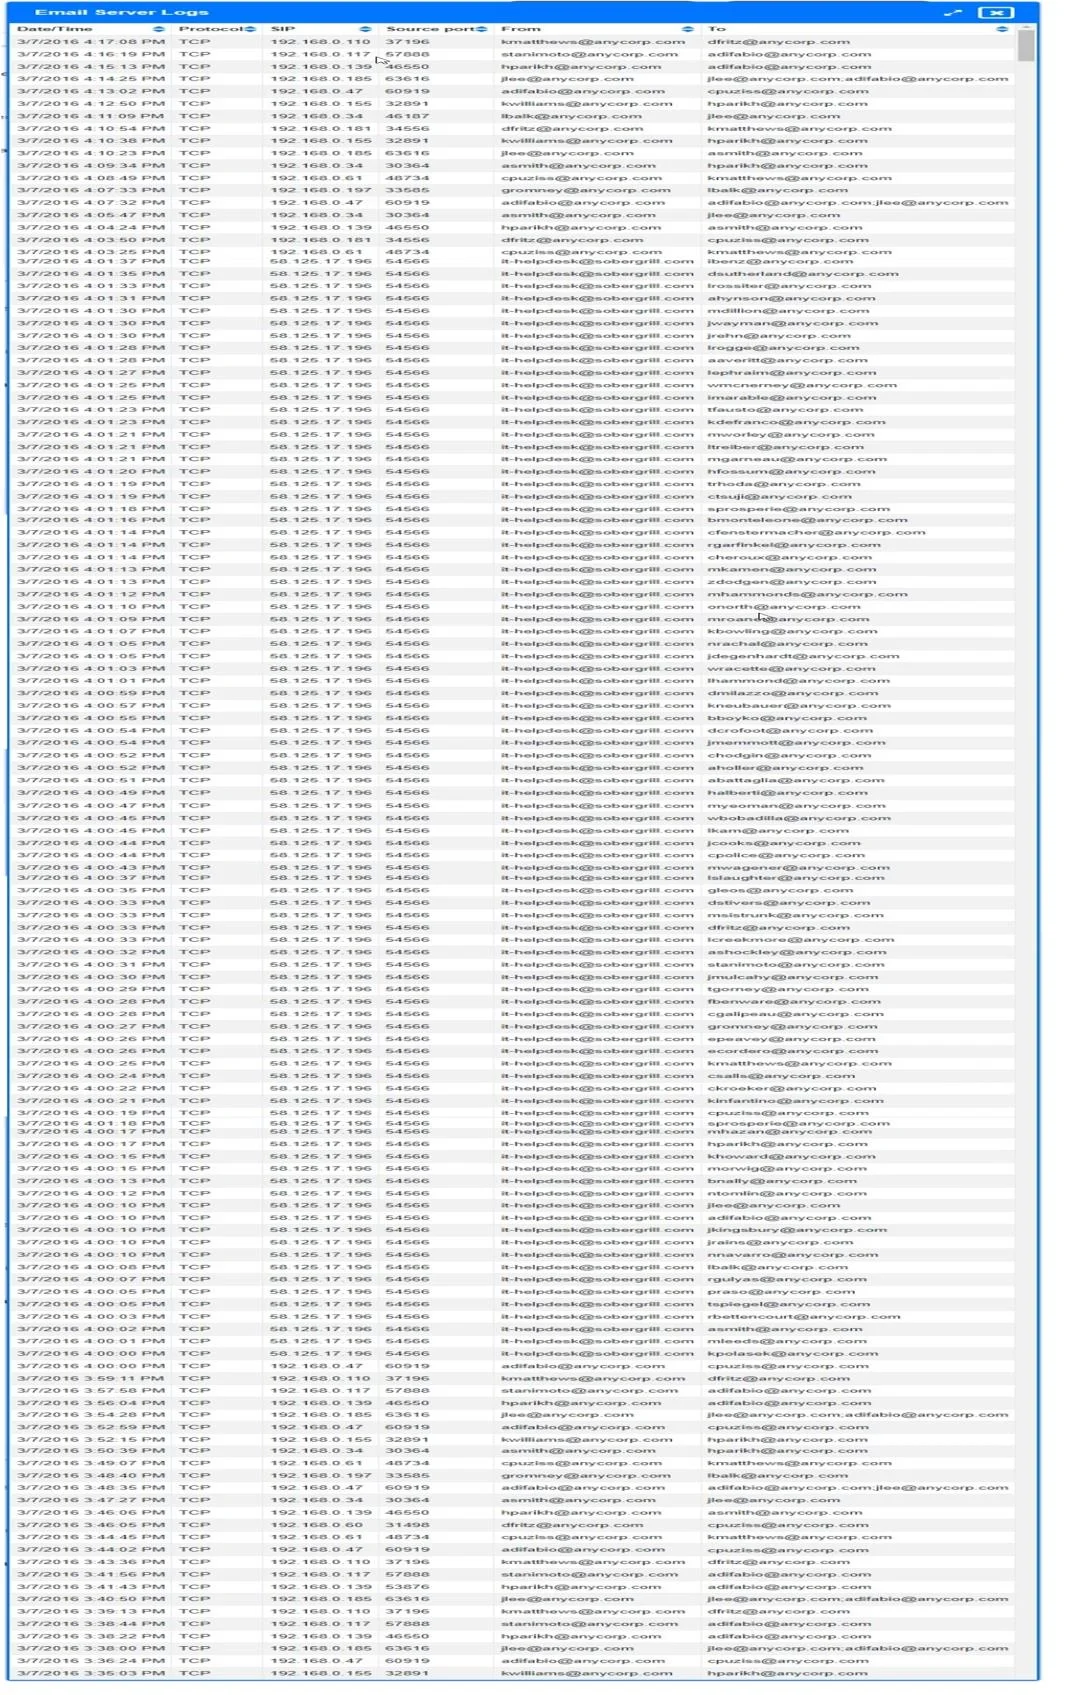
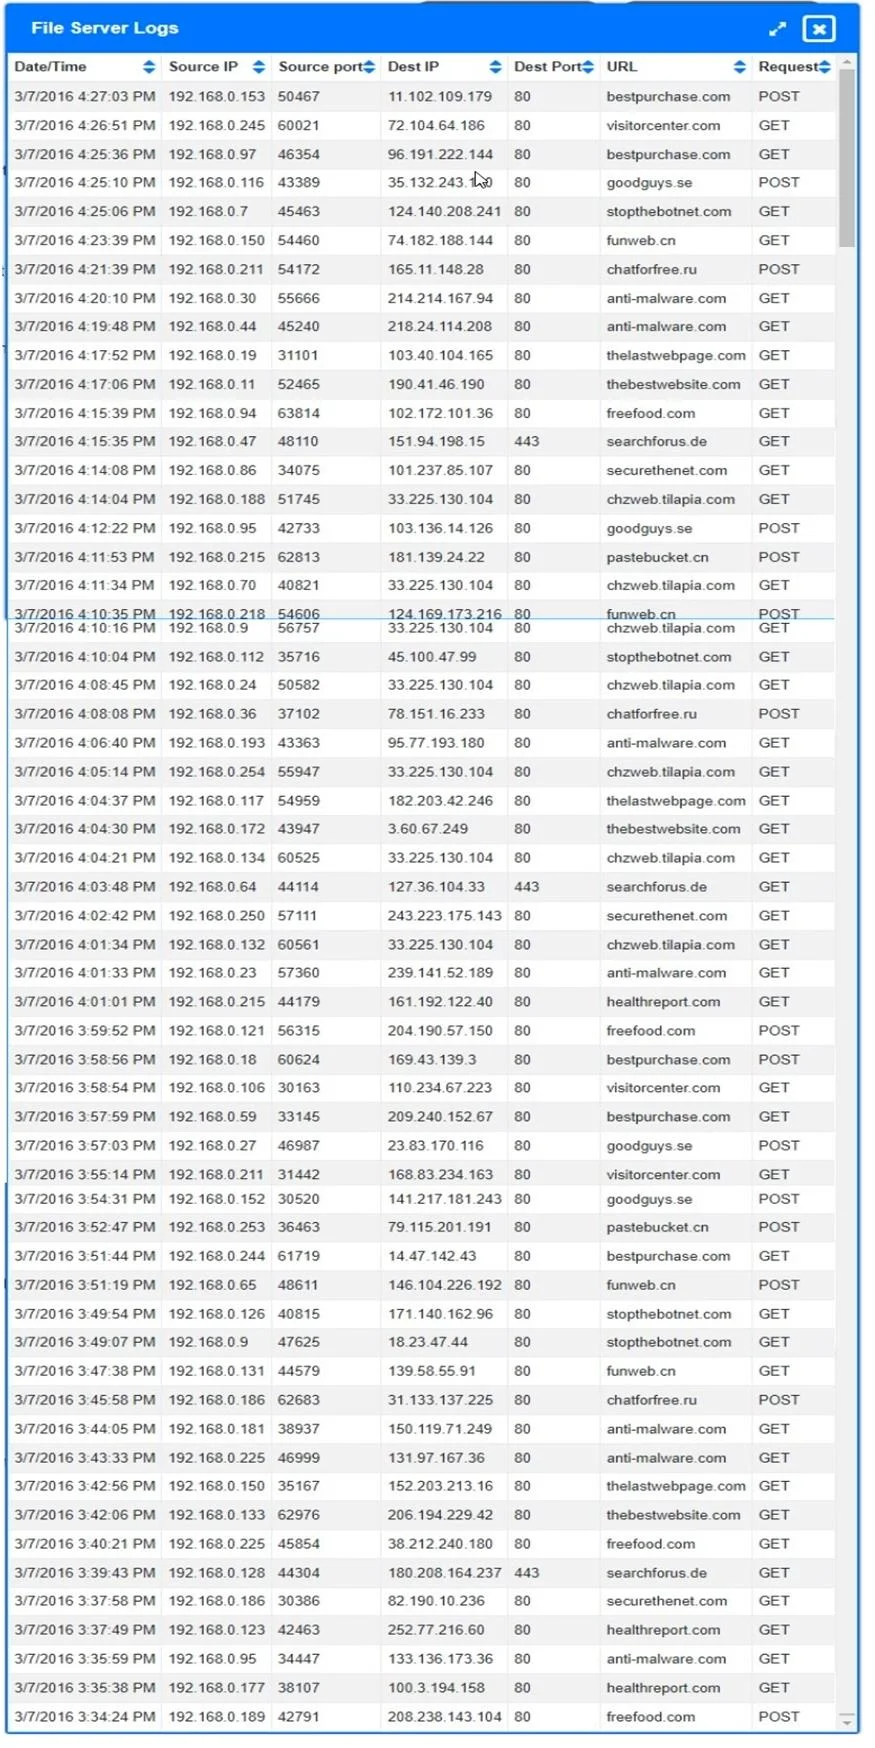
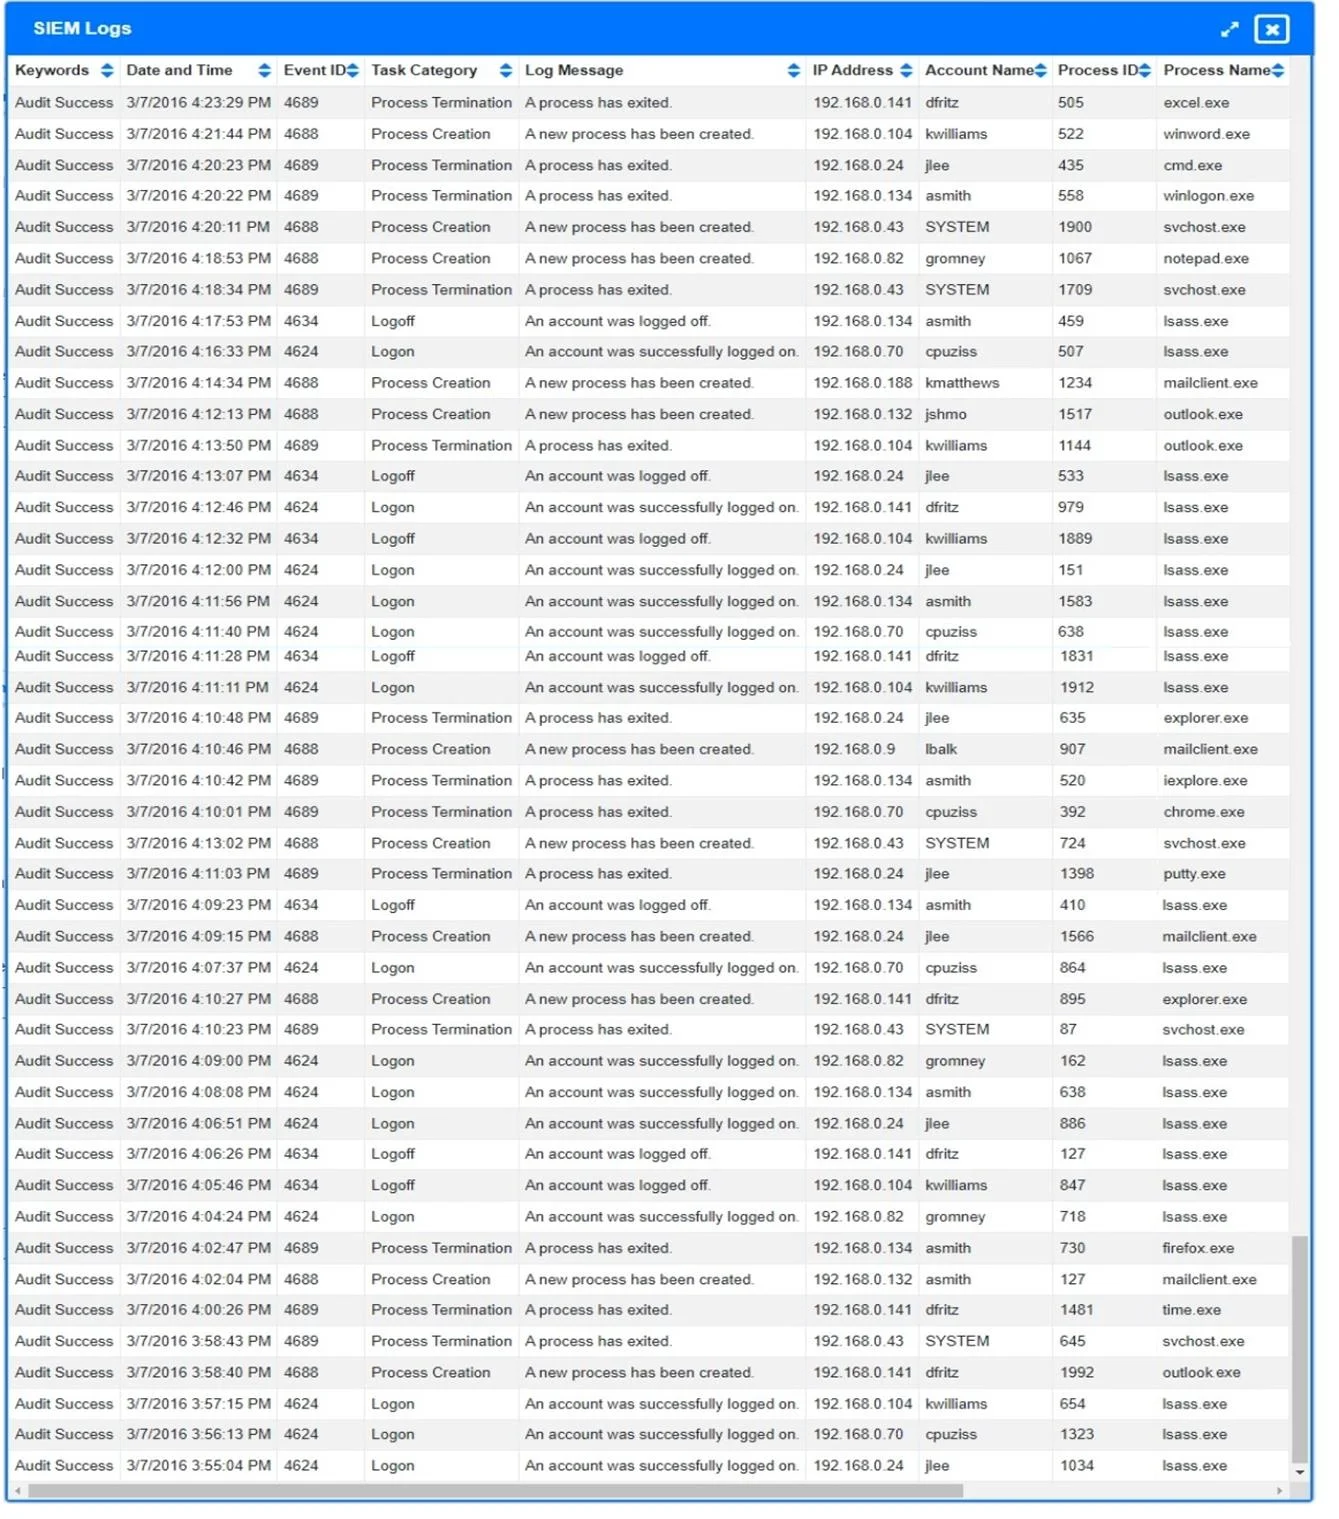
This is a simulation-based question from the CompTIA Security+ exam that requires candidates to analyze log files, email headers, endpoint detection reports, or SIEM data to extract specific incident response metrics. The correct answers are derived by carefully reviewing the provided simulation data: typically a proxy/web filter log shows how many employees clicked the phishing link, an endpoint protection or AV log reveals how many workstations had malware installed, and a process/file execution log identifies the malware executable name. These answers cannot be stated definitively without the actual simulation interface, but the methodology involves correlating HTTP GET requests to the malicious URL (clicks), successful payload execution events (installations), and the specific .exe filename flagged in alerts.
Topics
Community Discussion
No community discussion yet for this question.