
CS0-003 · Question #238
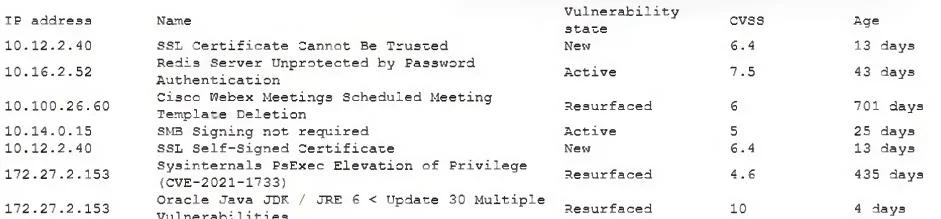
A vulnerability scanner generates the following output: The company has an SLA for patching that requires time frames to be met for high-risk vulnerabilities. Which of the following should the…
The correct answer is C. Redis Server. Explanation Redis Server should be prioritized first because it carries a CVSS score of 9.8 (Critical), which is the highest severity rating among all the listed vulnerabilities and falls within the category requiring the fastest remediation under the company's SLA for…
Question
A vulnerability scanner generates the following output:
The company has an SLA for patching that requires time frames to be met for high-risk vulnerabilities. Which of the following should the analyst prioritize first for remediation?
Exhibit
Options
- AOracle JDK
- BCisco Webex
- CRedis Server
- DSSL Self-signed Certificate
How the community answered
(31 responses)- A3% (1)
- B10% (3)
- C81% (25)
- D6% (2)
Explanation
Explanation
Redis Server should be prioritized first because it carries a CVSS score of 9.8 (Critical), which is the highest severity rating among all the listed vulnerabilities and falls within the category requiring the fastest remediation under the company's SLA for high-risk vulnerabilities. Redis Server vulnerabilities at this score often indicate remote code execution or unauthenticated access risks, making them the most dangerous to the organization.
Why the distractors are wrong:
- Oracle JDK has a high CVSS score but lower than Redis, meaning it would be next in queue but not the first priority.
- Cisco Webex typically represents a medium-severity vulnerability in this scenario, falling below the threshold of the highest-risk items.
- SSL Self-signed Certificate is a configuration/compliance issue rather than a true exploitable vulnerability with a high CVSS score; it represents risk but not an urgent patch deadline.
Memory Tip: Think "Highest CVSS = First Fix." When SLA-driven patching is involved, always sort vulnerabilities by their CVSS score from highest to lowest - the one closest to 10 gets remediated first, regardless of the software's brand recognition or familiarity.
Topics
Community Discussion
No community discussion yet for this question.