
CompTIA
CAS-005 · Question #476
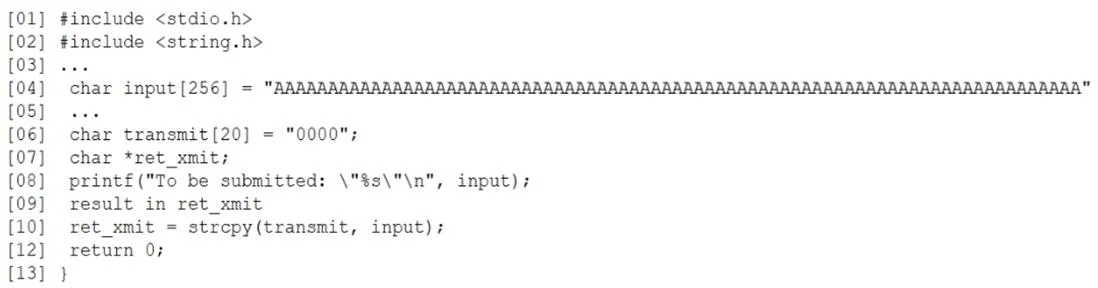
Based on the results of a SAST report on a legacy application, a security engineer is reviewing the following snippet of code flagged as vulnerable: Which of the following is the vulnerable line of…
The correct answer is E. Line [10]. The use of strcpy in line 10 is vulnerable because it does not check the size of the destination buffer, leading to a potential buffer overflow when copying the large input string into the smaller
Submitted by rachelw· Mar 6, 2026Security Engineering
Question
Based on the results of a SAST report on a legacy application, a security engineer is reviewing the following snippet of code flagged as vulnerable:
Which of the following is the vulnerable line of code that must be changed?
Exhibits
Options
- ALine [02]
- BLine [04]
- CLine [07]
- DLine [08]
- ELine [10]
How the community answered
(14 responses)- B7% (1)
- C7% (1)
- E86% (12)
Explanation
The use of strcpy in line 10 is vulnerable because it does not check the size of the destination buffer, leading to a potential buffer overflow when copying the large input string into the smaller
Community Discussion
No community discussion yet for this question.