
CAS-005 · Question #328
The results of an internal audit indicate several employees reused passwords that were previously included in a published list of compromised passwords. The company has the following employee…
The correct answer is A. Increase the minimum age to two days. B. Increase the history to 20. Increase the minimum age to two days: Setting a minimum age for passwords ensures that users cannot immediately change their password multiple times in succession to cycle through the password history and reuse a previous password. By increasing the minimum age to two days, it…
Question
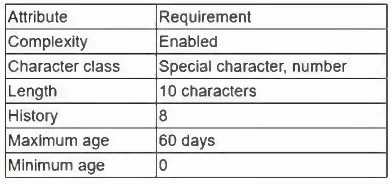
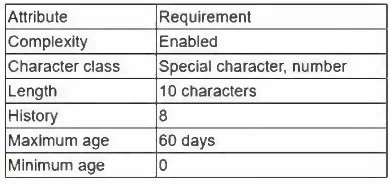
The results of an internal audit indicate several employees reused passwords that were previously included in a published list of compromised passwords. The company has the following employee password policy:
Which of the following should be implemented to best address the password reuse issue? (Choose two.)
Exhibits
Options
- AIncrease the minimum age to two days.
- BIncrease the history to 20.
- CIncrease the character length to 12.
- DAdd case-sensitive requirements to character class.
- EDecrease the maximum age to 30 days.
- FRemove the complexity requirements.
- GIncrease the maximum age to 120 days.
How the community answered
(46 responses)- A85% (39)
- D4% (2)
- E9% (4)
- G2% (1)
Explanation
Increase the minimum age to two days: Setting a minimum age for passwords ensures that users cannot immediately change their password multiple times in succession to cycle through the password history and reuse a previous password. By increasing the minimum age to two days, it prevents this kind of behavior and enforces better password reuse discipline. Increase the history to 20: The password history determines how many previous passwords are remembered by the system to prevent reuse. By increasing the history to 20, users are forced to create a significantly different password for a longer period, reducing the likelihood of reusing compromised passwords.
Community Discussion
No community discussion yet for this question.