
CAS-005 · Question #325
A security architect needs to enable a container orchestrator for DevSecOps and SOAR initiatives. The engineer has discovered that several Ansible YAML files used for the automation of configuration…
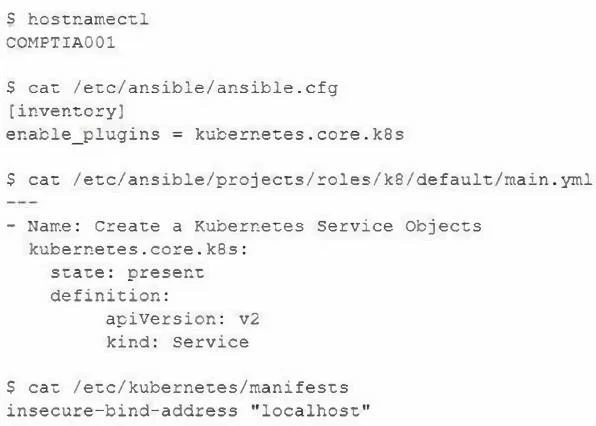
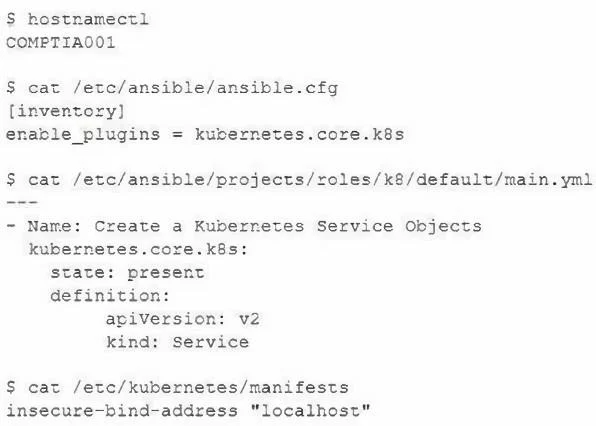
The correct answer is D. Update or remove the ansible.cfg file. The Ansible configuration file (/etc/ansible/ansible.cfg) contains an enable_plugins directive that allows Kubernetes modules to interact with Kubernetes resources. However, it does not enforce secure practices for managing these interactions, which could potentially expose…
Question
A security architect needs to enable a container orchestrator for DevSecOps and SOAR initiatives. The engineer has discovered that several Ansible YAML files used for the automation of configuration management have the following content:
Which of the following should the engineer do to correct the security issues presented within this content?
Exhibits
Options
- AUpdate the kubernetes.core.k8s module to kubernetes.core.k8s_service in the
- BUpdate the COMPTIA001 hostname to localhost using the hostnamectl command.
- CUpdate the module to state: absent in the file.
- DUpdate or remove the ansible.cfg file.
- EUpdate the insecure-bind-address from localhost to the COMPTIA001 in the manifests
How the community answered
(42 responses)- A17% (7)
- B2% (1)
- C2% (1)
- D71% (30)
- E7% (3)
Explanation
The Ansible configuration file (/etc/ansible/ansible.cfg) contains an enable_plugins directive that allows Kubernetes modules to interact with Kubernetes resources. However, it does not enforce secure practices for managing these interactions, which could potentially expose sensitive data or allow unauthorized changes if not correctly configured or overly permissive. The insecure configuration in the Ansible YAML file or the ansible.cfg file should be reviewed or updated to enforce stricter security. Specifically, the configuration might inadvertently expose Kubernetes services to untrusted sources, and enabling plugins like kubernetes.core.k8s without sufficient control could lead to vulnerabilities. Updating or removing the ansible.cfg file ensures that secure defaults are applied, or more secure plugin configurations can be explicitly added, addressing the underlying issue.
Community Discussion
No community discussion yet for this question.