
CAS-005 · Question #291
An auditor is reviewing the logs from a web application to determine the source of an incident. The web application architecture includes an internet-accessible application load balancer, a number…
The correct answer is A. Enable the X-Forwarded-For header at the load balancer. In a tiered setup behind a proxy or load balancer, the web servers’ REMOTE_ADDR will only ever show the balancer’s IP, not the true client’s. By configuring the load balancer to inject the X-Forwarded-For HTTP header with the original client IP, that value can be logged by the…
Question
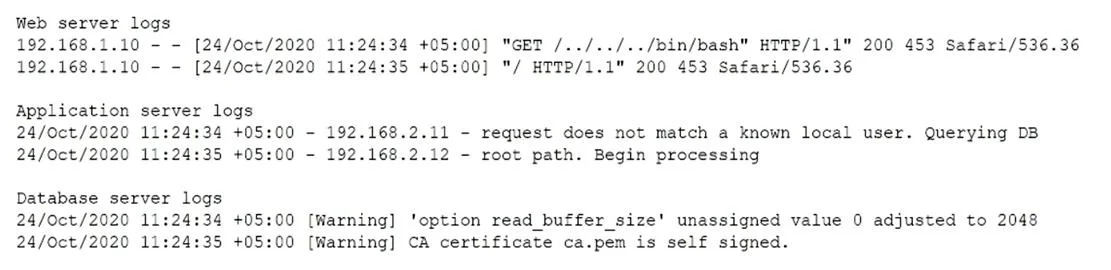
An auditor is reviewing the logs from a web application to determine the source of an incident. The web application architecture includes an internet-accessible application load balancer, a number of web servers in a private subnet, application servers, and one database server in a tiered configuration. The application load balancer cannot store the logs. The following are sample log snippets:
Which of the following should the auditor recommend to ensure future incidents can be traced back to the sources?
Exhibits
Options
- AEnable the X-Forwarded-For header at the load balancer.
- BInstall a software-based HIDS on the application servers.
- CInstall a certificate signed by a trusted CA.
- DUse stored procedures on the database server.
- EStore the value of the $_SERVER['REMOTE_ADDR'] received by the web servers.
How the community answered
(25 responses)- A56% (14)
- B4% (1)
- C20% (5)
- D12% (3)
- E8% (2)
Explanation
In a tiered setup behind a proxy or load balancer, the web servers’ REMOTE_ADDR will only ever show the balancer’s IP, not the true client’s. By configuring the load balancer to inject the X-Forwarded-For HTTP header with the original client IP, that value can be logged by the web servers (and propagated downstream), ensuring every request can be traced back to the real source address.
Community Discussion
No community discussion yet for this question.