
CAS-005 · Question #247
A company reduced its staff 60 days ago, and applications are now starting to fail. The security analyst is investigating to determine if there is malicious intent for the application failures. The…
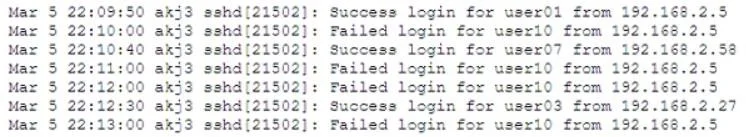
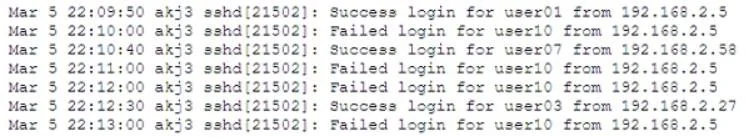
The correct answer is A. The user's account was set as a service account. The logs show repeated failed logins for from the same IP (192.168.2.5) at regular intervals, suggesting an automated process. This behavior is characteristic of a service account that is still active after a staff reduction, but likely disabled or removed, causing dependent…
Question
A company reduced its staff 60 days ago, and applications are now starting to fail. The security analyst is investigating to determine if there is malicious intent for the application failures. The security analyst reviews the following logs:
Which of the following is the most likely reason for the application failures?
Exhibits
Options
- AThe user's account was set as a service account.
- BThe user's home directory was deleted.
- CThe user does not have sudo access.
- DThe root password has been changed.
How the community answered
(37 responses)- A76% (28)
- B3% (1)
- C8% (3)
- D14% (5)
Explanation
The logs show repeated failed logins for from the same IP (192.168.2.5) at regular intervals, suggesting an automated process. This behavior is characteristic of a service account that is still active after a staff reduction, but likely disabled or removed, causing dependent applications to fail.
Community Discussion
No community discussion yet for this question.