
CompTIA
CAS-005 · Question #206
A security engineer is reviewing the SIEM logs after a server crashed. The following list of events represents the timeline of actions collected from the SIEM: Which of the following TTPs is most…
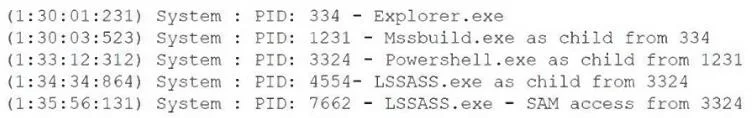
The correct answer is B. Credential dumping. The logs show processes associated with credential dumping, specifically LSASS.exe access, which is commonly targeted to extract stored credentials from memory for later use by attackers.
Submitted by mateo_ar· Mar 6, 2026Security Operations
Question
A security engineer is reviewing the SIEM logs after a server crashed. The following list of events represents the timeline of actions collected from the SIEM:
Which of the following TTPs is most likely associated with this SIEM log?
Exhibits
Options
- ALateral movement
- BCredential dumping
- CData exfiltration
- DLOLBins use
How the community answered
(32 responses)- A9% (3)
- B81% (26)
- C3% (1)
- D6% (2)
Explanation
The logs show processes associated with credential dumping, specifically LSASS.exe access, which is commonly targeted to extract stored credentials from memory for later use by attackers.
Community Discussion
No community discussion yet for this question.