
CAS-005 · Question #186
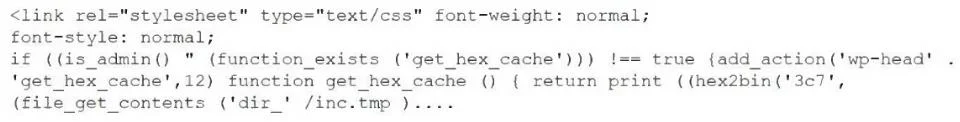
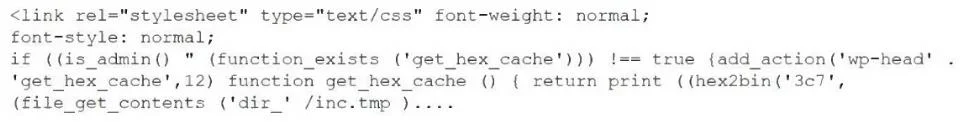
A security administrator is reviewing the following code snippet from a website component: A review of the inc.tmp file shows the following: Which of the following is most likely the reason for…
The correct answer is A. A content management solution plug-in has been exploited. The code snippet includes obfuscated PHP code that loads and executes content from a temporary file (inc.tmp) via hex2bin(file_get_contents(...)), often seen in web malware injections. This strongly suggests that a CMS plug-in has been exploited to inject malicious code into…
Question
A security administrator is reviewing the following code snippet from a website component:
A review of the inc.tmp file shows the following:
Which of the following is most likely the reason for inaccuracies?
Exhibits
Options
- AA content management solution plug-in has been exploited.
- BA search engine's bots are being blocked at the firewall.
- CThe relevant stylesheet has become corrupted.
- DThe WAF is configured to be in transparent mode.
How the community answered
(37 responses)- A54% (20)
- B14% (5)
- C5% (2)
- D27% (10)
Explanation
The code snippet includes obfuscated PHP code that loads and executes content from a temporary file (inc.tmp) via hex2bin(file_get_contents(...)), often seen in web malware injections. This strongly suggests that a CMS plug-in has been exploited to inject malicious code into the website.
Community Discussion
No community discussion yet for this question.