
CAS-005 · Question #137
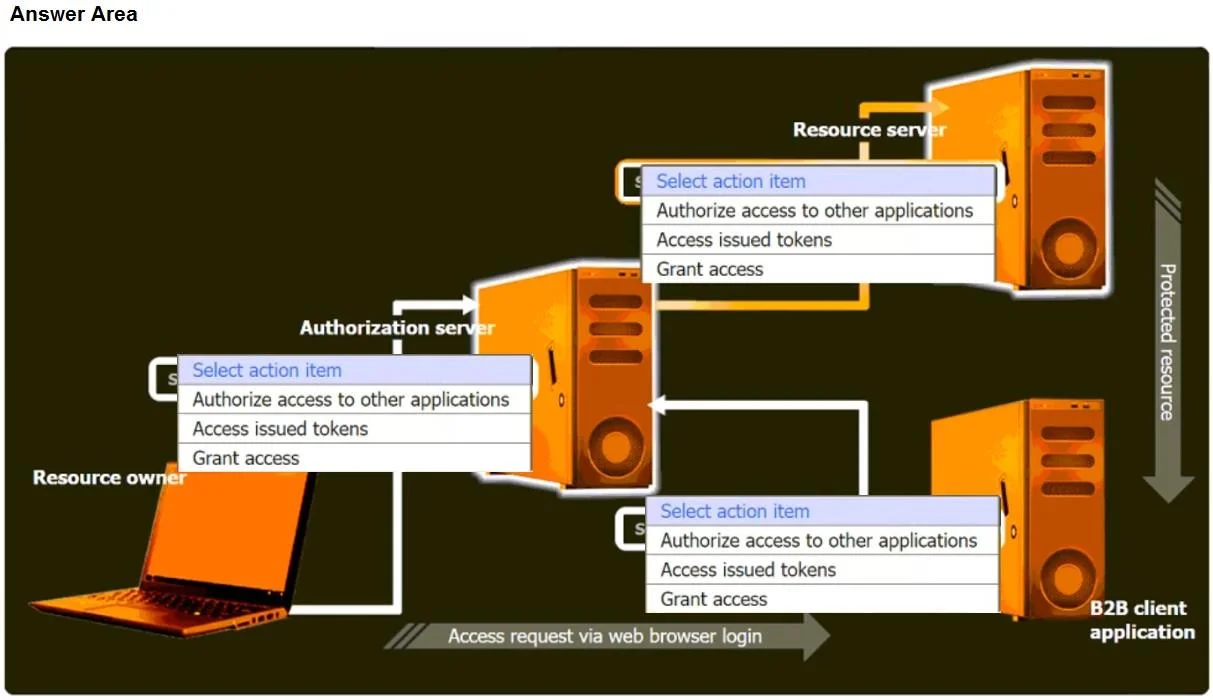
SIMULATION You are tasked with integrating a new B2B client application with an existing OAuth workflow that must meet the following requirements: - The application does not need to know the users'…
The correct configuration maps each OAuth 2.0 role to its proper function: the Resource Server hosts protected user data and authorizes access to other applications, the Authorization Server issues and manages tokens (access tokens, refresh tokens) after validating consent, and…
Question
Exhibits
Explanation
The correct configuration maps each OAuth 2.0 role to its proper function: the Resource Server hosts protected user data and authorizes access to other applications, the Authorization Server issues and manages tokens (access tokens, refresh tokens) after validating consent, and the B2B Client Application redirects users to the Authorization Server to obtain delegated access without ever handling user credentials. This satisfies all three requirements: credentials are never exposed to the client app, the Authorization Server orchestrates the user approval/consent interaction, and scopes on the issued tokens limit what data the client can access.
Topics
Community Discussion
No community discussion yet for this question.