
AZ-700 · Question #315
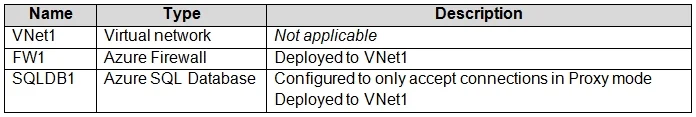
You have an Azure subscription that contains the resources shown in the following table. You need to configure FW1 to filter traffic that originates from VNet1 and targets the FQDN of SQLDB1. Which…
The correct answer is C. application. Azure Firewall application rules support FQDN-based filtering and include native support for SQL FQDNs (port 1433) via the 'Sql' service tag or explicit FQDN entries. Application rules are the correct layer for filtering outbound traffic to specific fully qualified domain names…
Question
You have an Azure subscription that contains the resources shown in the following table. You need to configure FW1 to filter traffic that originates from VNet1 and targets the FQDN of SQLDB1. Which type of rule should you use?
Exhibit
Options
- ADNAT
- Bnetwork
- Capplication
- Dinfrastructure
How the community answered
(32 responses)- A3% (1)
- B6% (2)
- C81% (26)
- D9% (3)
Explanation
Azure Firewall application rules support FQDN-based filtering and include native support for SQL FQDNs (port 1433) via the 'Sql' service tag or explicit FQDN entries. Application rules are the correct layer for filtering outbound traffic to specific fully qualified domain names regardless of IP address changes. DNAT rules redirect inbound traffic and cannot filter by FQDN in this manner. Network rules filter by IP address and port but do not resolve or match FQDNs natively for SQL. Infrastructure rules are implicit built-in rules for Azure platform traffic, not user-defined FQDN filtering.
Community Discussion
No community discussion yet for this question.