
AZ-700 · Question #202
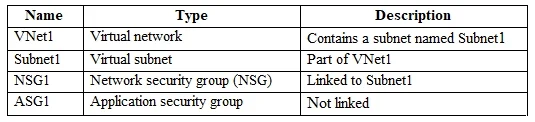
You have an Azure subscription that contains the resources shown in the following table. Subnet1 contains three virtual machines that host an app named App1. App1 is accessed by using the SFTP…
The correct answer is B. From each virtual machine, associate the network interface to ASG1. To ensure inbound SFTP connections are managed by ASG1 with minimal administrative effort, given an existing NSG rule targeting ASG1, an association step is required.
Question
You have an Azure subscription that contains the resources shown in the following table. Subnet1 contains three virtual machines that host an app named App1. App1 is accessed by using the SFTP protocol. From NSG1, you configure an inbound security rule named Rule2 that allows inbound SFTP connections to ASG1. You need to ensure that the inbound SFTP connections are managed by using ASG1. The solution must minimize administrative effort. What should you do?
Exhibit
Options
- AFrom NSG1, modify the priority of Rule2.
- BFrom each virtual machine, associate the network interface to ASG1.
- CFrom Subnet1, create a subnet delegation.
- DFrom ASG1, modify the role assignments.
How the community answered
(61 responses)- A16% (10)
- B72% (44)
- C3% (2)
- D8% (5)
Why each option
To ensure inbound SFTP connections are managed by ASG1 with minimal administrative effort, given an existing NSG rule targeting ASG1, an association step is required.
Modifying the priority of Rule2 would change its order of evaluation within NSG1 but would not make the rule applicable to the virtual machines unless their network interfaces are associated with ASG1.
For an inbound Network Security Group (NSG) rule, such as Rule2, that specifies an Application Security Group (ASG1) as its destination, the network interfaces of the target virtual machines must be explicitly associated with ASG1. This direct association allows the NSG rule to correctly identify and apply security policies to the VMs hosting App1.
Subnet delegation is a feature used to allow specific Azure services to be deployed into a subnet and does not relate to associating virtual machines with Application Security Groups for network security rules.
Modifying role assignments controls who has permissions to manage resources (RBAC) and does not configure network traffic flow or the application of network security rules to virtual machines via ASGs.
Concept tested: Application Security Group association to NICs
Source: https://learn.microsoft.com/en-us/azure/virtual-network/application-security-groups
Community Discussion
No community discussion yet for this question.