
AZ-305 · Question #87
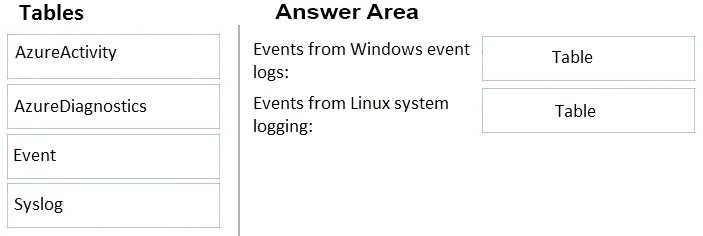
Drag and Drop Question You have an Azure subscription. The subscription contains Azure virtual machines that run Windows Server 2016 and Linux. You need to use Azure Log Analytics design an alerting…
The correct answer is Event; Syslog. The 'Event' table in Log Analytics stores Windows Event Log data collected from Windows Server machines, making it the correct table to query for security-related events on Windows Server 2016 (e.g., Security event logs). The 'Syslog' table stores log data collected from Linux…
Question
Exhibit
Answer Area
Drag items
Correct arrangement
- Event
- Syslog
Explanation
The 'Event' table in Log Analytics stores Windows Event Log data collected from Windows Server machines, making it the correct table to query for security-related events on Windows Server 2016 (e.g., Security event logs). The 'Syslog' table stores log data collected from Linux machines via the Syslog daemon, making it the appropriate table for security-related events on Linux systems. Together, these two tables cover the Windows and Linux virtual machines described in the scenario.
Topics
Community Discussion
No community discussion yet for this question.