
AZ-305 · Question #312
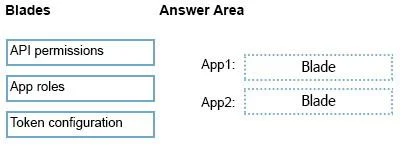
Drag and Drop Question You have two app registrations named App1 and App2 in Azure AD. App1 supports role-based access control (RBAC) and includes a role named Writer. You need to ensure that when…
The correct answer is App1: App roles; App2: API permissions. App1 uses the 'App roles' blade to define and expose the 'Writer' role, making it available as a claimable role in tokens. App2 uses the 'API permissions' blade to request (grant) permission to that role defined in App1, so when App2 authenticates, Azure AD includes the Writer…
Question
Exhibit
Answer Area
Drag items
Correct arrangement
- App1: App roles
- App2: API permissions
Explanation
App1 uses the 'App roles' blade to define and expose the 'Writer' role, making it available as a claimable role in tokens. App2 uses the 'API permissions' blade to request (grant) permission to that role defined in App1, so when App2 authenticates, Azure AD includes the Writer role claim in the issued token. This two-step process - defining the role on the resource app (App1) and assigning/requesting it on the client app (App2) - is how application-level RBAC works in Azure AD for app-to-app scenarios.
Topics
Community Discussion
No community discussion yet for this question.